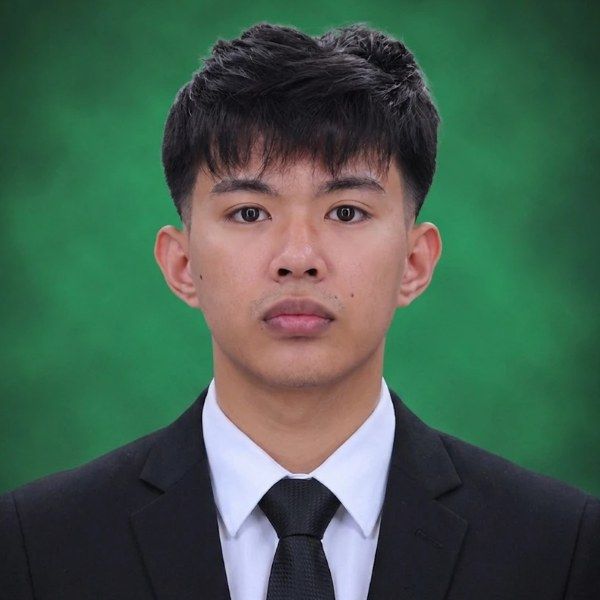
Moises Ceazar Del Mundo
Open to OJT / Internship · 2026–2027

Moises Ceazar Del Mundo

Aspiring SOC Analyst — a fourth-year Information Security student who deployed a live security monitoring platform for a city government.

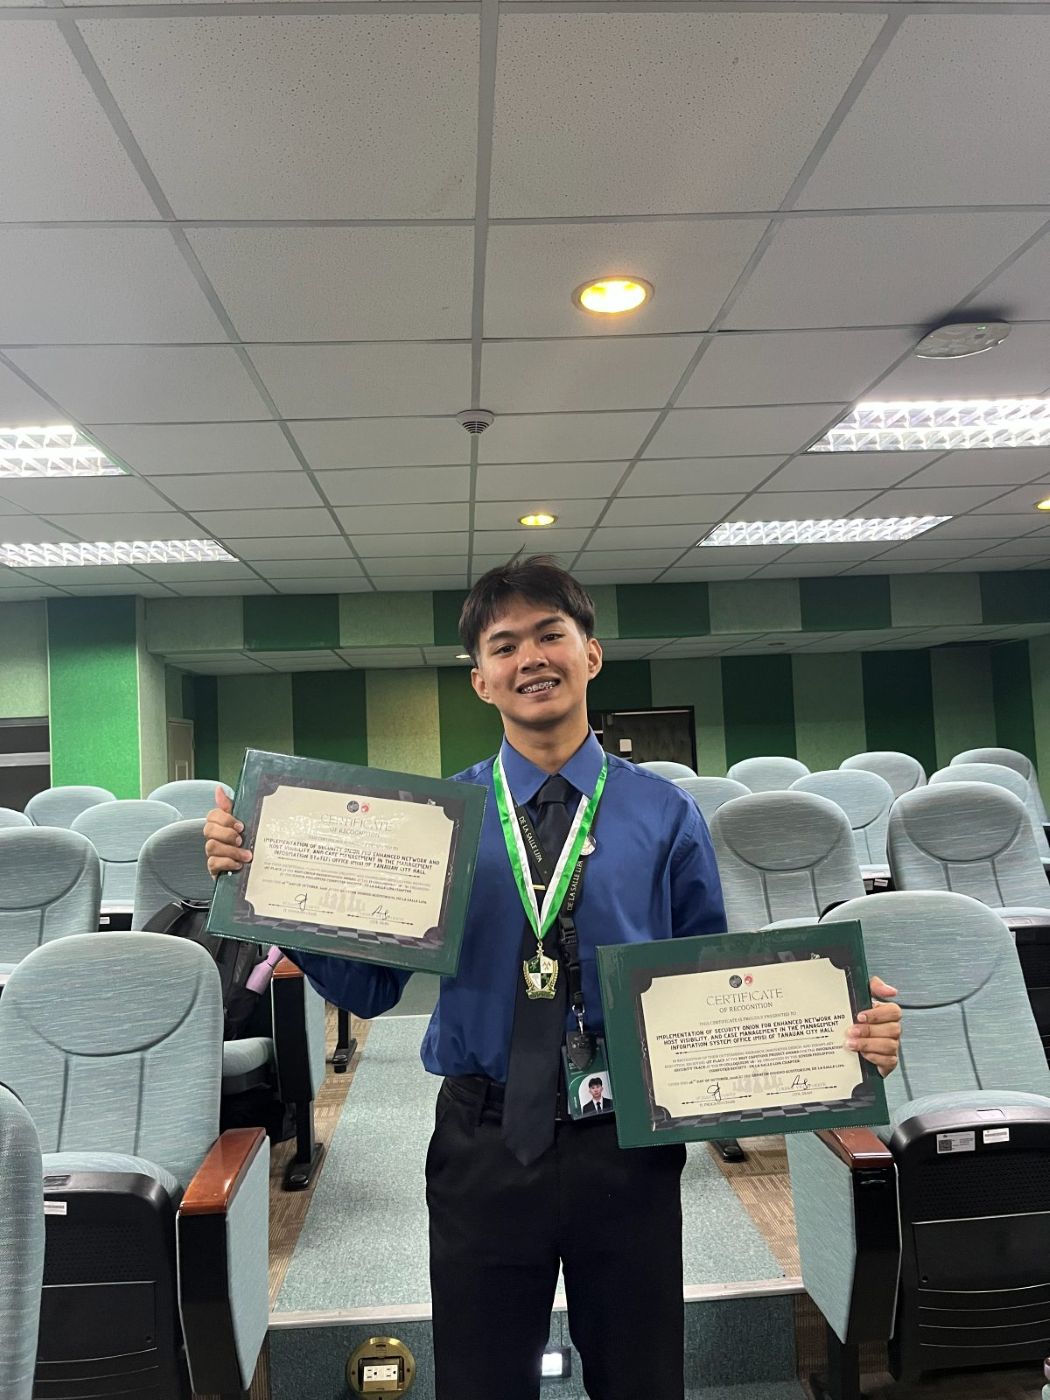
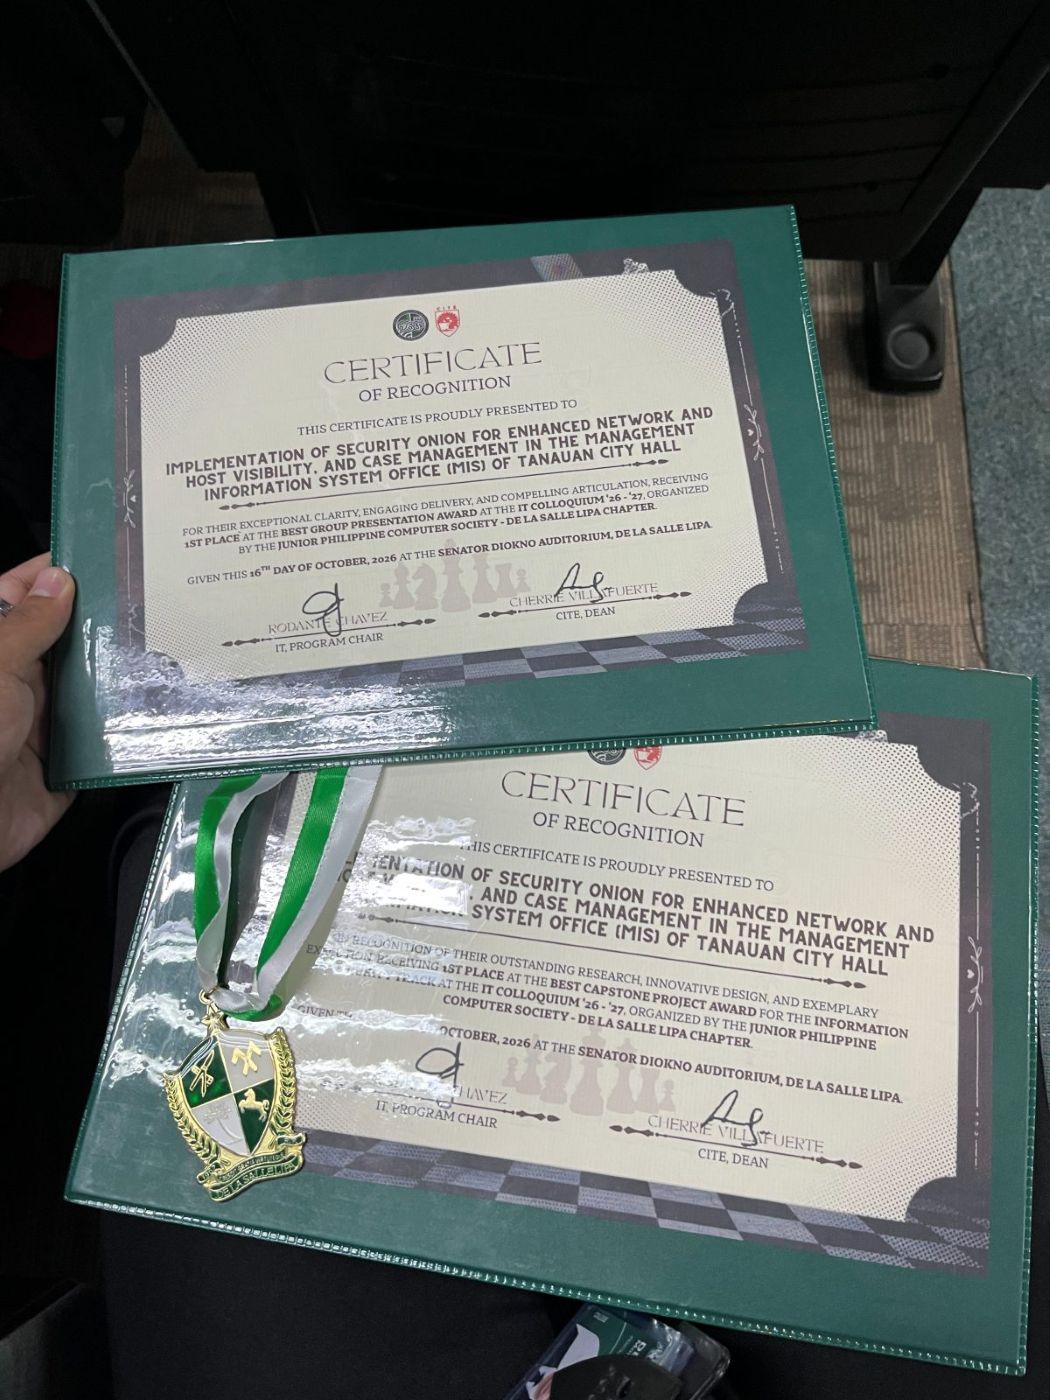
  • 🏆1st Place, Best Capstone — Information Security Track, IT Colloquium '26–'27
  • 🛡️ISC2 Certified in Cybersecurity (CC) · Appkademiya CCP
  • 📈9.7M events monitored in a live city government deployment
Moises Ceazar Del Mundo
Aspiring SOC Analyst · Open to OJT
● Open to Work
8
Certs
3.38
GWA
9
Projects
CC
ISC2
Security OnionWazuhElastic SuricataZeekNessus
Security Onion ·
Wazuh SIEM ·
Kibana ·
Zeek ·
Suricata IDS/IPS ·
Nessus ·
Proxmox VE ·
Sophos Central ·
Fortinet FortiGate ·
T-Pot Honeypot ·
MITRE ATT&CK ·
LetsDefend ·
ISC2 CC ·
Blue Team Ops ·
Threat Detection ·
Incident Response ·
Phishing Analysis ·
Malware Analysis ·
Security Onion ·
Wazuh SIEM ·
Kibana ·
Zeek ·
Suricata IDS/IPS ·
Nessus ·
Proxmox VE ·
Sophos Central ·
Fortinet FortiGate ·
T-Pot Honeypot ·
MITRE ATT&CK ·
LetsDefend ·
ISC2 CC ·
Blue Team Ops ·
Threat Detection ·
Incident Response ·
Phishing Analysis ·
Malware Analysis ·
01 — Featured

Award-Winning Capstone

A live security monitoring platform deployed into a real city government network — built, tested, hardened, and handed over.

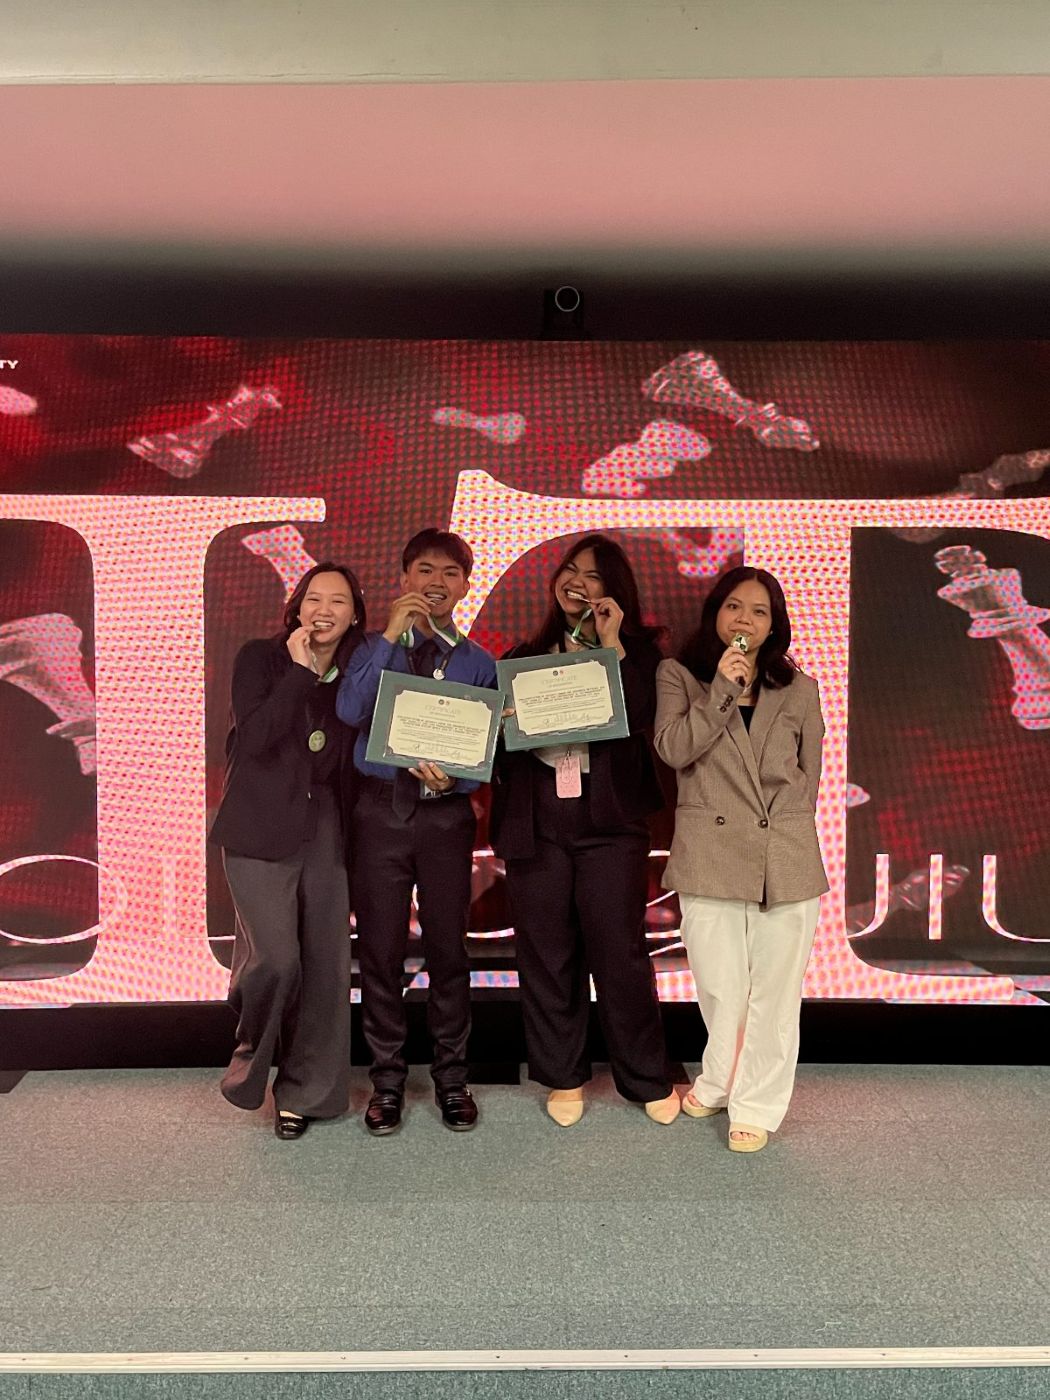
🏆 1st Place · Best Capstone Project — Information Security Track🏆 1st Place · Best Group Presentation
Featured · Capstone Project · IT Colloquium '26–'27

Security Onion for Network & Host Visibility and Case Management — MIS Office, Tanauan City Hall

Deployed Security Onion into a live government network that had only a perimeter firewall and relied on external advisories for threat awareness. Built network visibility (Suricata, Zeek via SPAN port), host visibility (Elastic Agent on five pilot endpoints), custom Kibana host and network monitoring dashboards, STRIDE- and ATT&CK-mapped detection rules for brute force, port scanning, USB exfiltration and C2 traffic, plain-language Telegram alerts via ElastAlert 2, and case management with Security Onion Cases, grounded in NIST CSF 2.0 and the Philippine NCSP 2023–2028. Validated against five simulated attack scenarios, then hardened the platform after the defense with MFA, secrets storage and key-only SSH. Formally endorsed by the MIS Department Head for continued use.
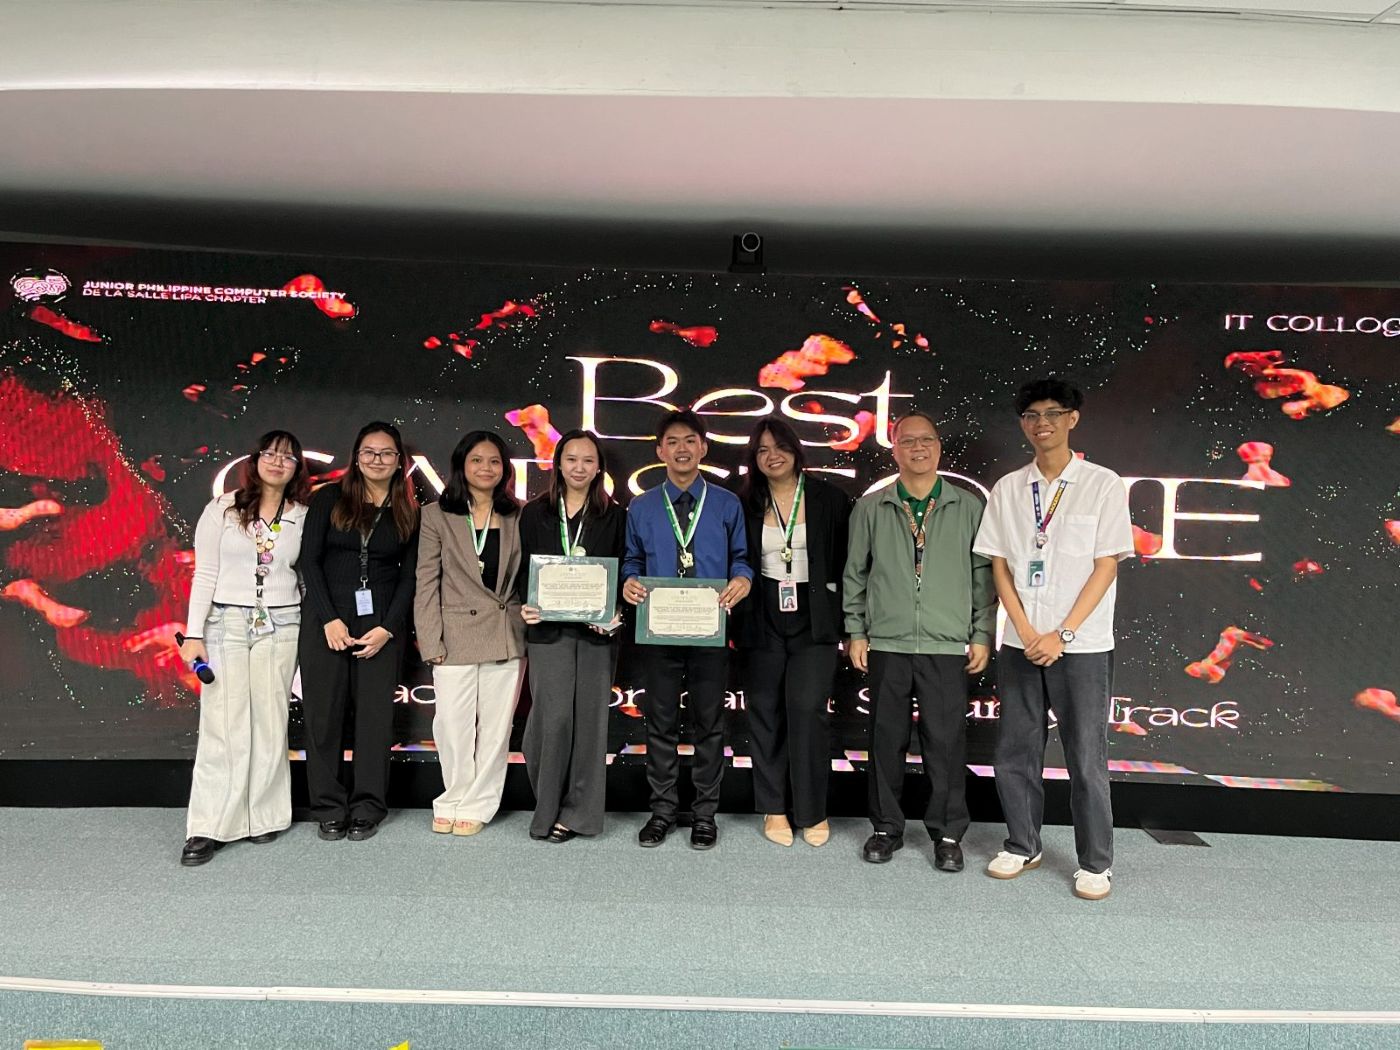
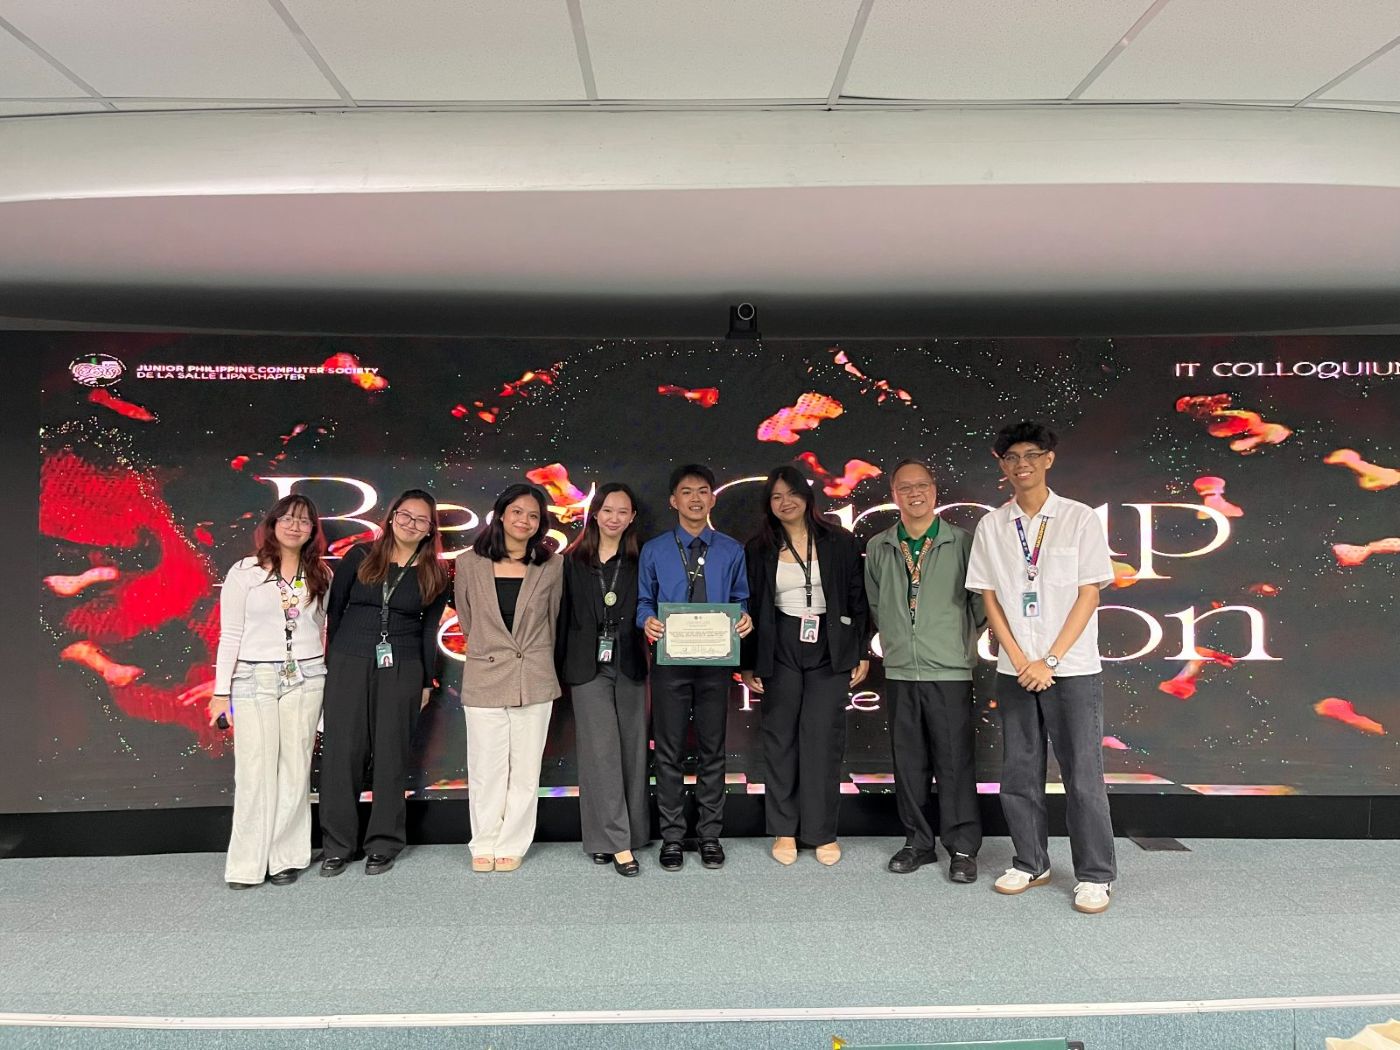
Group 6, De La Salle Lipa — Atienza · Babasa · Del Mundo · Macandile
100%
Detection rate · 5 of 5 attack scenarios
~1.5 min
Average alert-to-Telegram time
9.7M
Events indexed in 4 days live
~10%
False positive rate after tuning
68→83
Lynis hardening index
₱0
Licensing cost · fully open source
First IT Colloquium of De La Salle Lipa · organized by JPCS – DLSL Chapter · Oct 16, 2026 · Senator Diokno Auditorium
02 — Experience

Hands-On Experience

Real deployments, industry mentorship and leadership — not just coursework.

Security Monitoring Deployment — Capstone Project (Group 6)
2025 – 2026 · Live Aug 2026
MIS Office, Tanauan City Hall · Real client deployment
  • Deployed Security Onion on the Tanauan City Hall network (Suricata, Zeek, Elastic Agent on five endpoints) with custom Kibana dashboards, ATT&CK-mapped detection rules and Telegram alerting.
  • 100% detection across five simulated attacks and 9.7M+ events indexed in four days live; endorsed by the MIS Department Head for continued use. See the full capstone ↑
Security OnionElastic StackSuricataZeekElastAlert 2NIST CSF 2.0
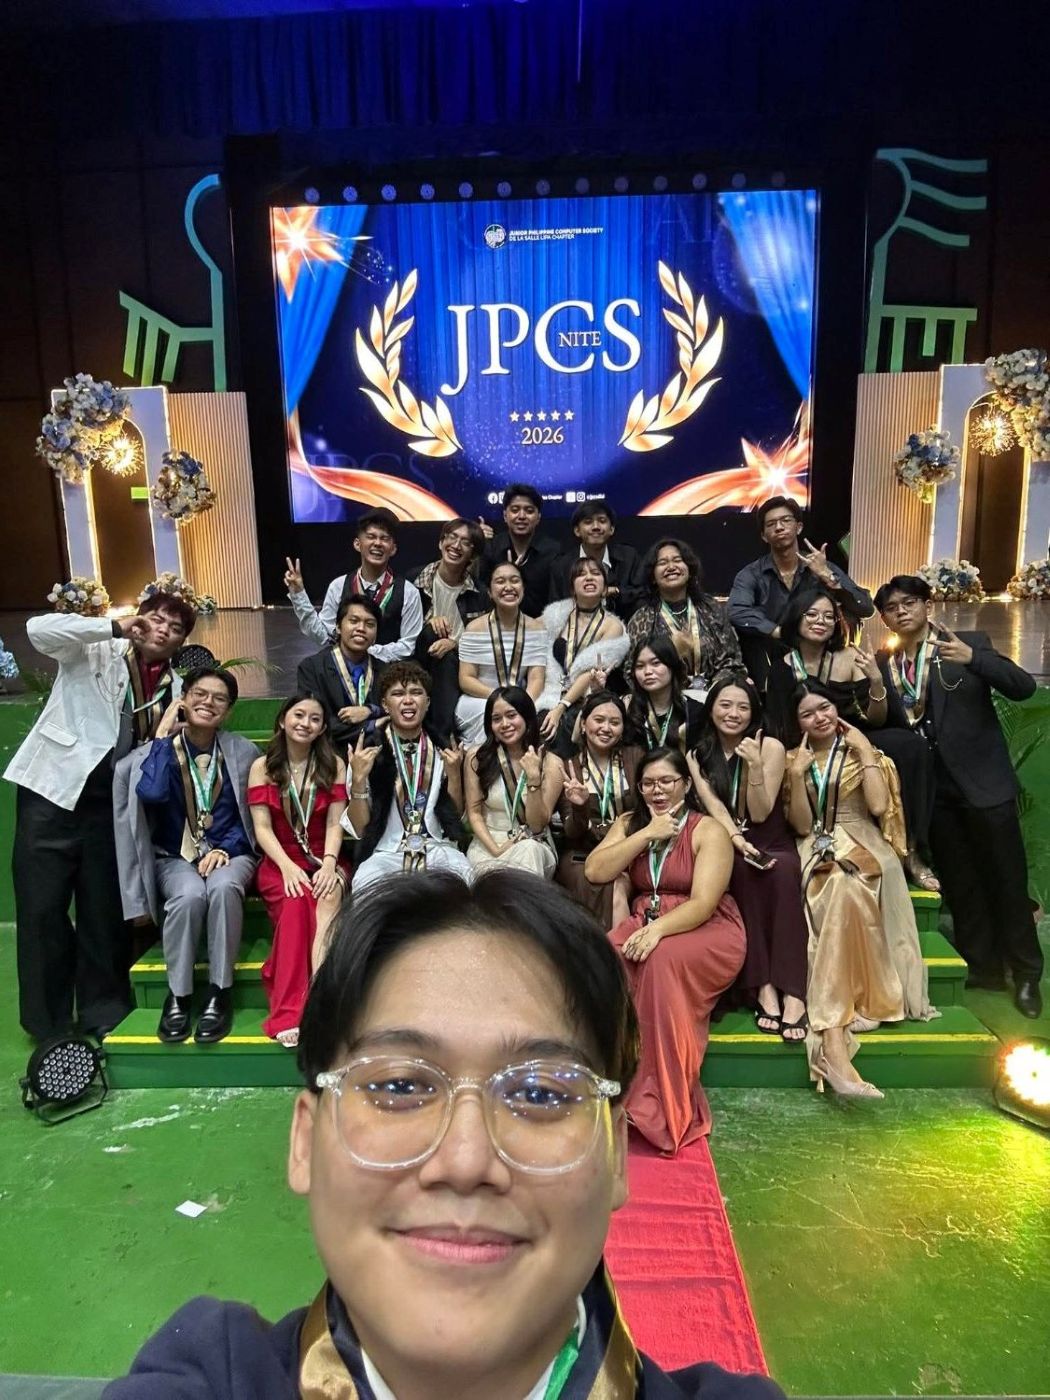
Project Head, Internal Affairs (IT) · previously 3rd Year IT Representative
AY 2025–2026 – Present
Junior Philippine Computer Society – De La Salle Lipa Chapter
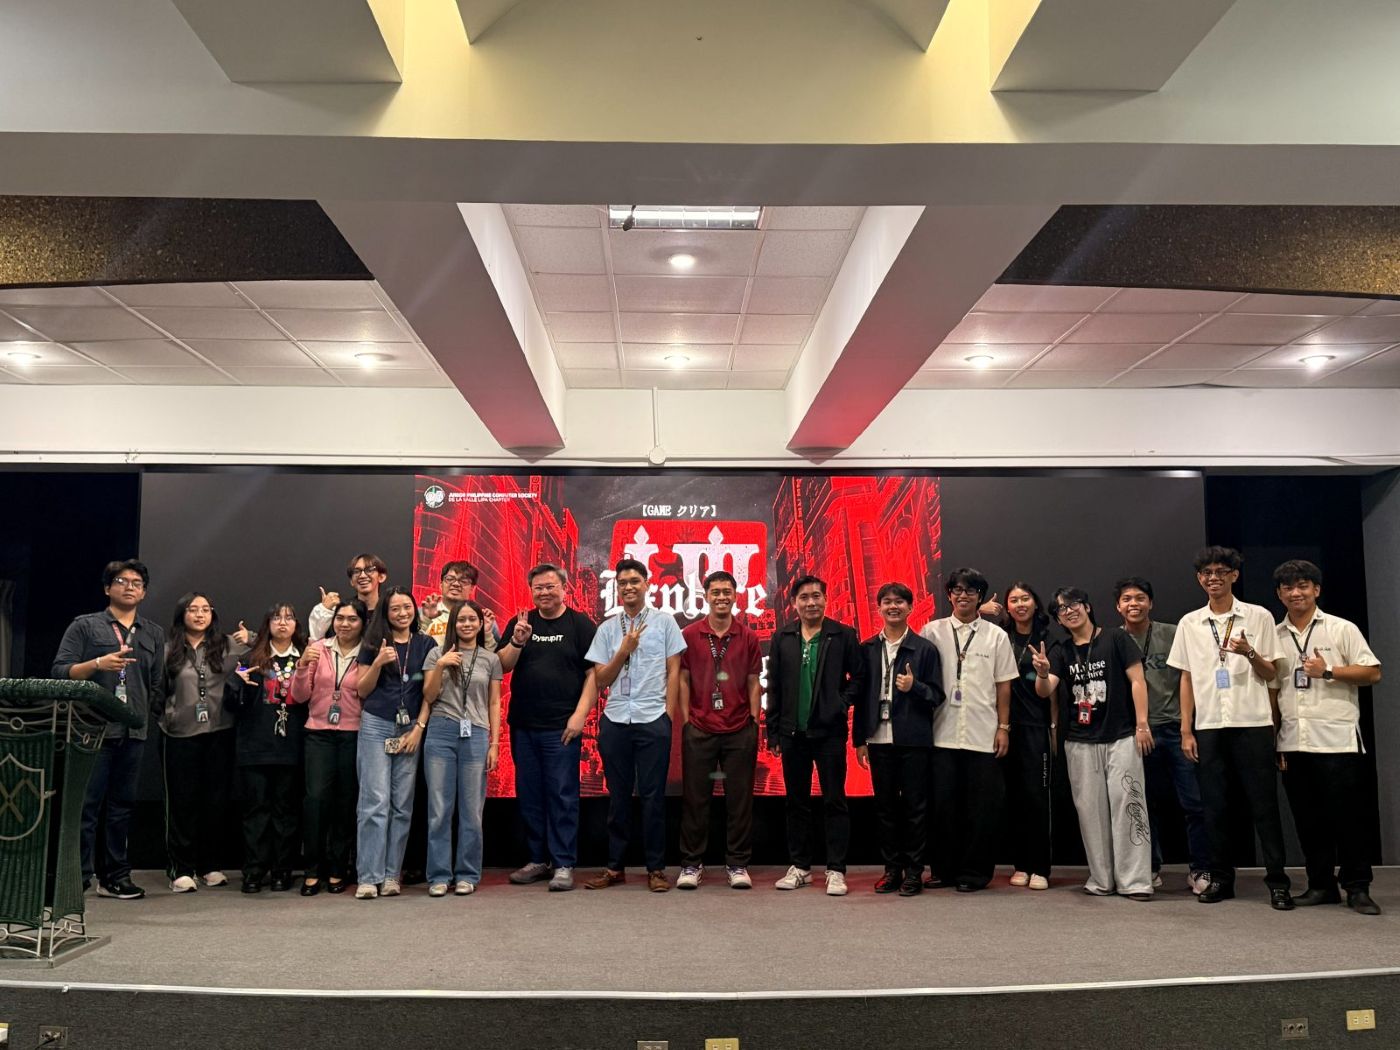
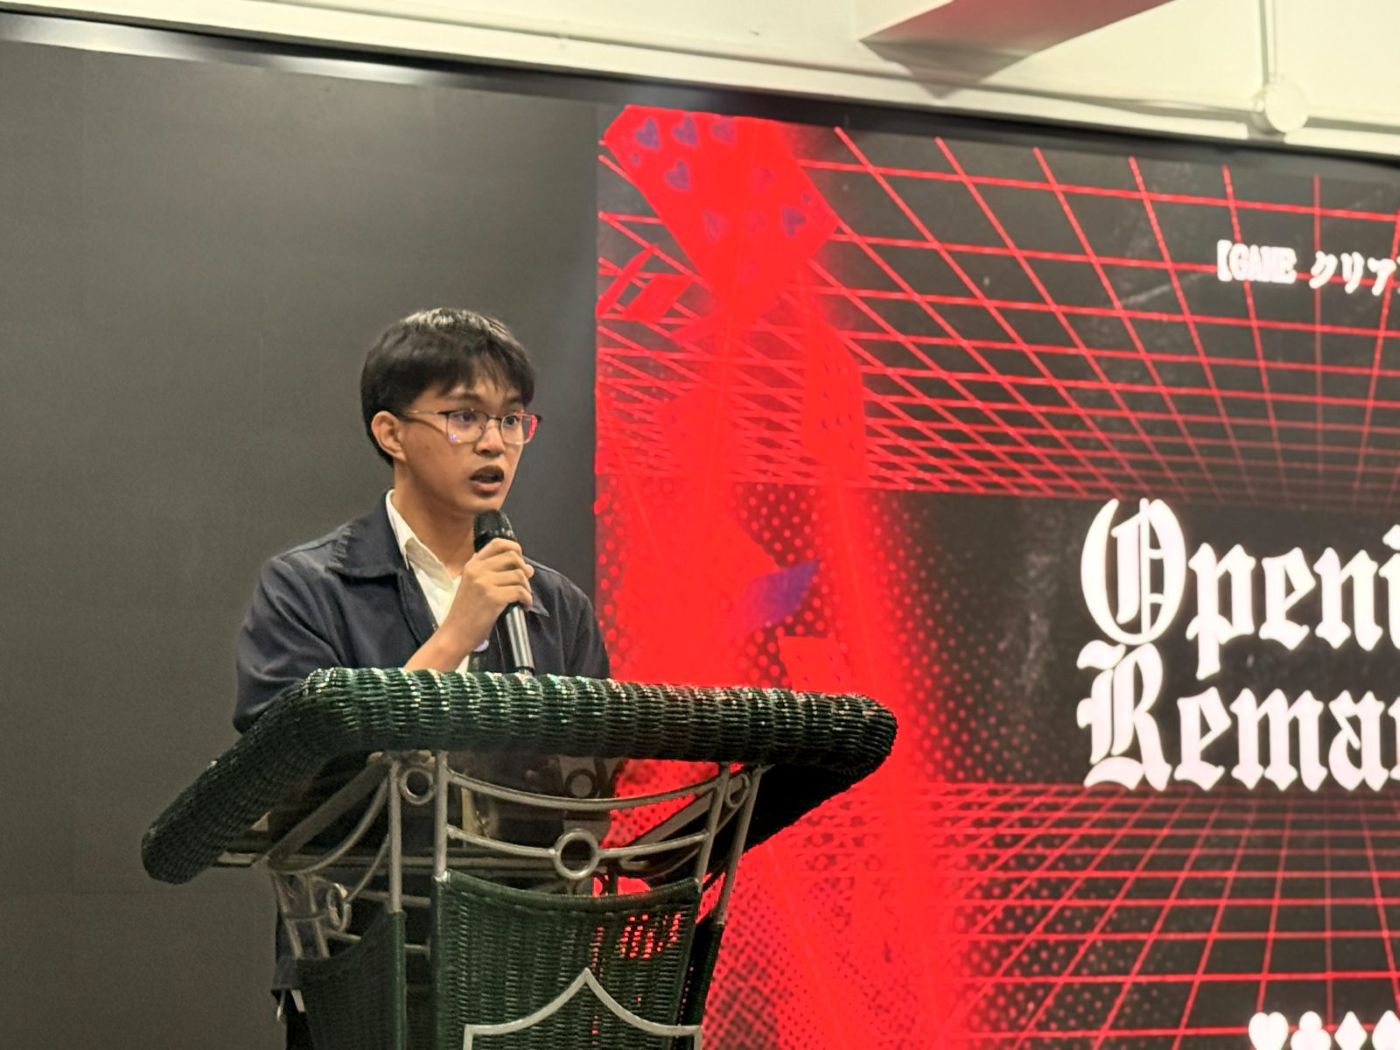
  • Lead student committees organizing department-wide IT workshops, technical seminars and academic competitions for 200+ attendees.
  • Write the documentation behind each event for administrative approval: concept papers, SWOT analyses, narrative reports and executive summaries.
  • Handle stakeholder communication and promotional media to drive student engagement.
Event PlanningConcept PapersSWOT AnalysisGoogle Workspace
Security Operations Center Lab Mentee
2025 – Present
DysrupIT × De La Salle Lipa Partnership · Industry mentorship
  • Deployed Action1 RMM across lab endpoints to find missing patches and vulnerabilities, run patch management and software deployment, and support remediation.
  • Ran controlled simulations — Nmap reconnaissance, Hydra credential brute-forcing, Telnet cleartext exposure — to evaluate NIDS/HIDS detection.
  • Analyzed processes, persistence and endpoint alerts with Windows Sysinternals and Sophos Central; triaged phishing via email-header analysis (SPF, DKIM, DMARC, ARC) and reviewed T-Pot honeypot attacker logs. Email header forensics ↗
Action1 RMMSophos CentralSysinternalsNmapHydraT-Pot
Community Service Lead — NSTP
2024
De La Salle Lipa · NSTP Community Service Learning
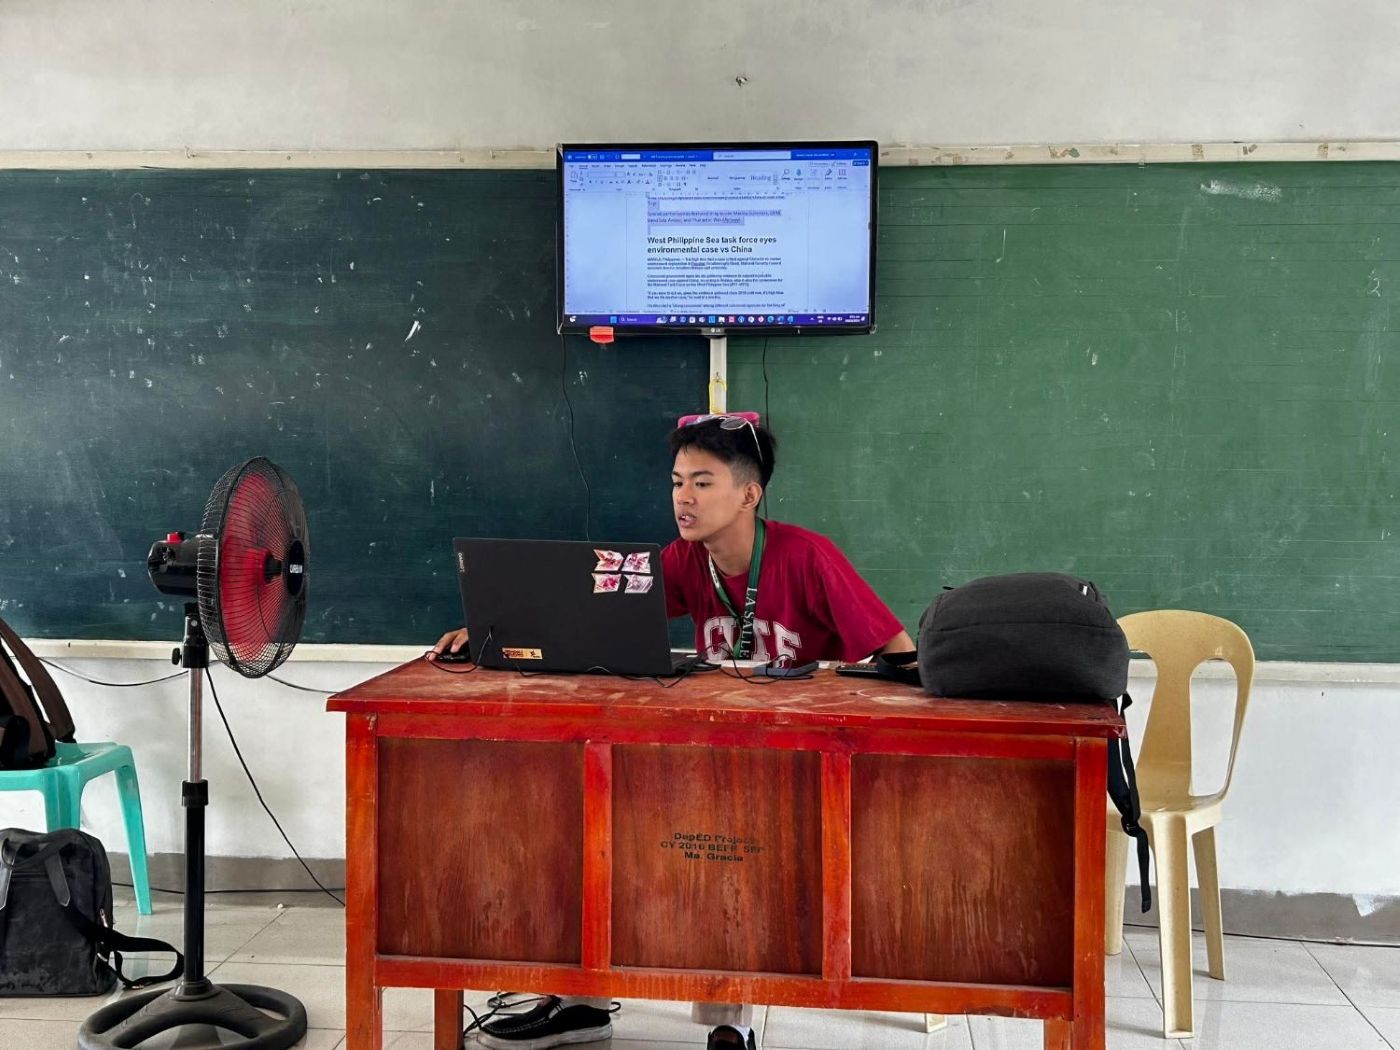
  • Spearheaded our group's community service at a public school, teaching students basic computer skills and Microsoft Office.
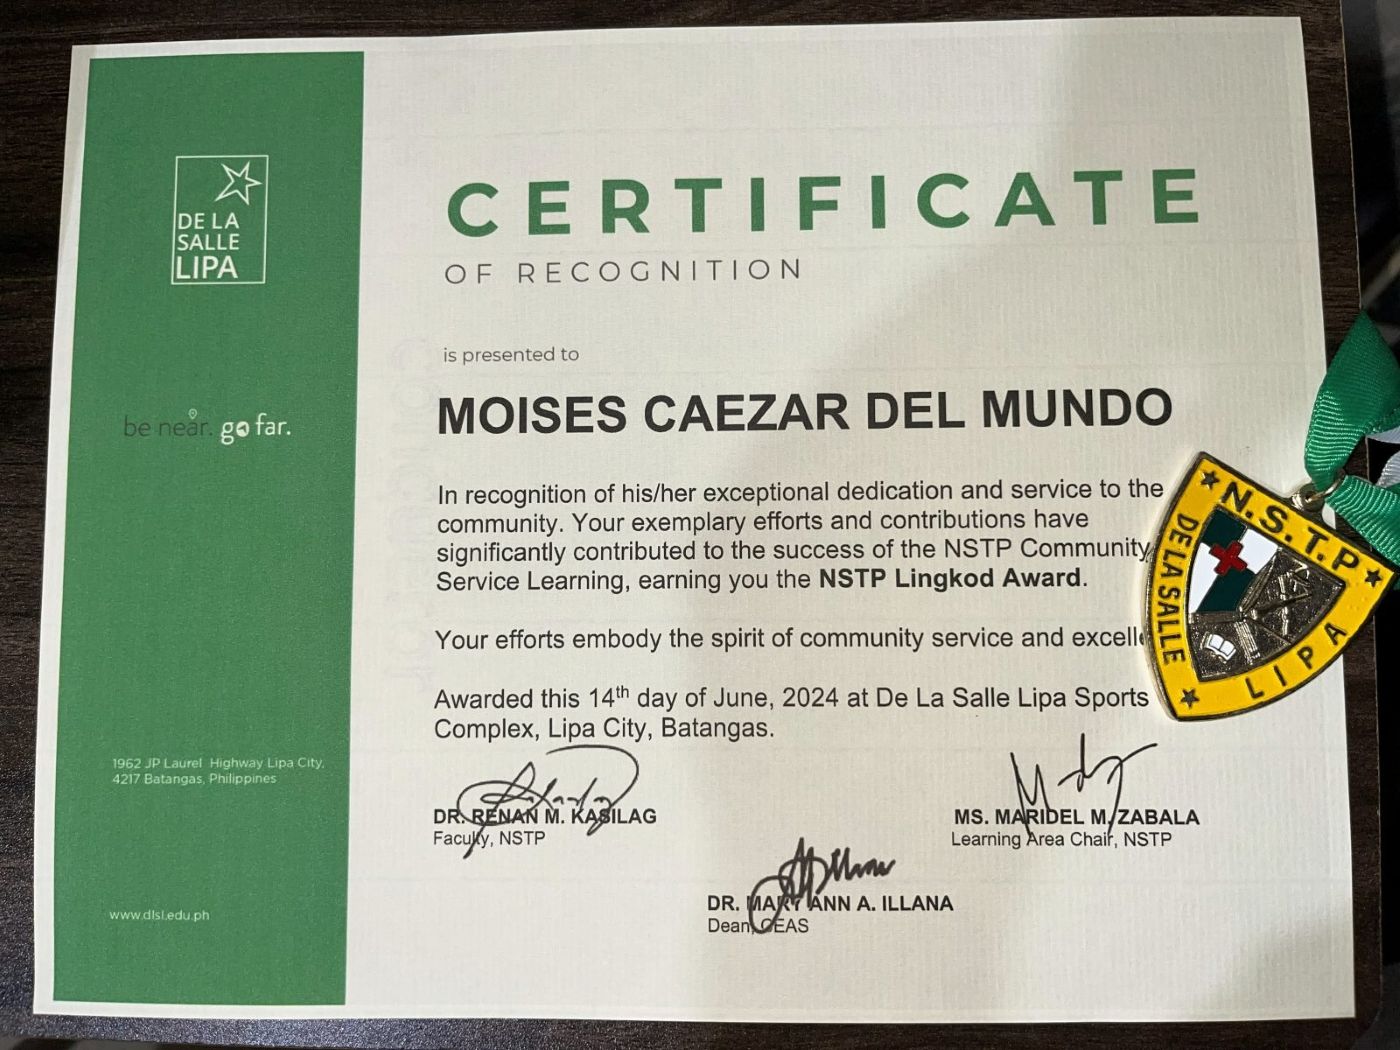
  • Received the NSTP Lingkod Award (June 14, 2024) for exceptional dedication and service to the community.
TeachingLeadershipCommunity Service
03 — About

Who I Am

I'm a fourth-year BSIT student majoring in Information Security at De La Salle Lipa, focused on Blue Team work: SOC monitoring, SIEM operations, threat detection, vulnerability assessment, and patch management. I learn best by building lab environments, attacking them in a controlled way, and documenting what the detections caught — and what they missed.

As a SOC lab mentee in the DysrupIT–DLSL partnership, I work hands-on with Security Onion, Wazuh, Kibana, Zeek, Suricata, T-Pot honeypots, Sophos Central, Action1 RMM, and Fortinet FortiGate. I independently built a Proxmox VE virtualized lab to run Nessus and OpenVAS vulnerability assessments and PowerShell remediation.

I keep my SOC Tier 1 skills sharp on LetsDefend — alert triage, phishing analysis, malware investigation, and incident handling — and have published 11 investigation writeups with MITRE ATT&CK mapping. Next milestone: CompTIA Security+.

Education
BSIT, Major in Information Security — De La Salle Lipa · 4th Year · Expected graduation June 2027
Location
Lipa City, Batangas, Philippines
Achievements
1st Place Best Capstone (Information Security Track) & 1st Place Best Group Presentation — IT Colloquium '26–'27 · Dean's Lister, all of first year (AY 2023–2024) · NSTP Lingkod Awardee (2024) · Top Student Awardee — IT Elective 2 (Information Security): Security Planning, Implementation & Audit (2026)
Target Role
SOC Analyst Intern · Blue Team · Cybersecurity OJT
Studying
Google Cybersecurity Certificate (in progress) · CompTIA Security+ · Splunk SIEM
Available
Internship / OJT · Philippines · 2026
04 — Projects

Lab Projects

Hands-on environments simulating real SOC workflows.

SIEMENDPOINT
Wazuh SIEM & Endpoint Monitoring Lab
Deployed a Wazuh agent–manager architecture across Windows and Linux VMs in Proxmox VE for centralized log analysis, active response and vulnerability monitoring. Implemented File Integrity Monitoring and wrote custom XML detection rules for critical file changes, potential privilege escalation and suspicious system activity.
Wazuh SIEM/XDRFIMCustom XML RulesActive ResponseProxmox VEWindowsLinux
SOC TRAININGWRITEUPS
LetsDefend SOC Investigation Writeups
Documented structured SOC Tier 1 investigations — alert triage, phishing email analysis, malware investigation, and incident handling in formal SOC analyst report format.
LetsDefendVirusTotalAny.runMITRE ATT&CKMXToolbox
SOC LABAUTOMATION
Security Onion Telegram Alerting
Automated real-time security alert forwarding from Security Onion (ElastAlert2 / Wazuh) to Telegram channels via Telegram Bot API, with MITRE ATT&CK-tagged detection rules covering SSH brute force, phishing C2, and port scanning.
Security OnionElastAlert2PythonTelegram Bot APIWazuh
SOC DEPLOYMENTDOCUMENTATION
Security Onion SOC Handbook — MIS Tanauan City Hall
Plain-language SOC user manual for City Hall MIS staff with no security background, covering system setup, login, Kibana dashboards, Telegram alerting, severity levels, six detection scenarios, alert response steps, and onboarding new endpoint agents.
Security OnionKibanaElastic AgentTelegram AlertsSOC Runbook
RECONNETWORK SECURITY
Nmap Network Reconnaissance & Service Exposure Lab
Authorized reconnaissance of two Linux targets in a Proxmox lab — host discovery, service/version enumeration, OS fingerprinting, and cURL service validation — documented in a technical assessment report that separates exposed services from confirmed vulnerabilities.
NmapKali LinuxProxmox VEcURLUbuntuDebian
SOC ANALYSISEMAIL
Email Header Forensics & Authentication Analysis
Practical SOC analysis of email routing paths, ESP delivery, cloud signature relays, and email authentication mechanics — evaluating SPF, DKIM, DMARC, and ARC across investigated cases.
SPFDKIMDMARCARCMail Header Forensics
ACADEMICSYSADMIN
Cybersecurity & System Administration Labs
Collection of academic labs covering cyber threat intelligence, CVE/vulnerability analysis, Windows Server Active Directory deployment, and Linux Apache web server hardening.
Active DirectoryLinuxApacheCVE ResearchThreat Intel
RESEARCHMALWARE
Fileless Malware Detection & Memory Forensics Research
Cybersecurity research proposal exploring fileless malware detection and neutralization using Sysmon, PowerShell Logging, and memory forensics in educational network environments.
SysmonPowerShell LoggingMemory Forensics
ACADEMICLEARNING LOG
IT Field Trip & Seminars Portfolio
Final-project portfolio documenting seminars, webinars, online courses, and certifications across cybersecurity, security operations, cloud, and AI — a record of continuous learning beyond the BSIT curriculum.
SeminarsWebinarsOnline CoursesCertificationsHTML
04b — Vulnerability Assessment

Nessus Vulnerability Playbooks

Real remediation playbooks from hands-on Nessus scanning — with before/after proof of resolution.

2
Critical
2
High Severity
18
Vulns Found
✓
Remediated
2
Targets Scanned
MEDIUM
CVSS 5.3
SMB Signing Not Required
Nessus Plugin #57608
Man-in-the-Middle SMB relay attack vector. Remediated via Group Policy and PowerShell enforcement of SMB signing.
SMB RelayMitMGroup PolicyPowerShell
LOW
CVSS 2.1
⏱️
ICMP Timestamp Remote Date Disclosure
Nessus Plugin #10114
System time exposure enabling Kerberos/TOTP bypass and uptime fingerprinting. Blocked via Windows Firewall ICMPv4 Type 13 rule.
ICMPFirewall RuleKerberosHardening
CRITICAL
CVSS 9.8
MS08-067 — RPC Remote Code Execution
Nessus Plugin #34477 · ECLIPSEDWING
Critical RCE via crafted RPC request with SYSTEM privileges. Equation Group exploit. Remediated via KB958644 security patch transferred via Python HTTP server.
RCEECLIPSEDWINGKB958644Python HTTP
HIGH
CVSS 8.8
MS17-010 — EternalBlue SMB RCE
Nessus Plugin #97833 · WannaCry Vector
SMBv1 multiple RCE vulnerabilities — WannaCry and NotPetya propagation vector. ETERNALBLUE, ETERNALCHAMPION, ETERNALROMANCE present. Remediated via KB4012598.
EternalBlueSMBv1WannaCryShadow Brokers
HIGH
CVSS 7.5
PetitPotam — NTLM Reflection EoP
Nessus Plugin #152102 · CVE-2021-36942
NTLM reflection elevation of privilege enabling AD CS certificate theft for lateral movement. Attacker forces host to authenticate to malicious server via EFSRPC.
NTLM RelayAD CSLateral MovementEoP
CRITICAL
CVSS 10.0
Unsupported Windows OS (Remote)
Nessus Plugin #108797
Windows Server 2003 is end-of-life and no longer receives security updates. Residual risk identified and documented. OS upgrade to supported version recommended.
EOL OSRisk AssessmentWindows 2003Documented
05 — Skills

Technical Arsenal

Built through real lab environments — not just coursework.

SIEM & Monitoring
Security OnionWazuh SIEM/XDRElasticsearchLogstashKibanaSuricataZeekElastAlert 2
Vulnerability Assessment
Tenable NessusOpenVASNmapPatch ManagementVulnerability RemediationCVE Analysis
Endpoint & Network
Sophos CentralAction1 RMMFortinet FortiGateFile Integrity MonitoringT-Pot HoneypotIDS/IPS
SOC Competencies
Alert TriageThreat DetectionLog AnalysisIOC IdentificationPhishing TriageEmail-Header AnalysisMalware InvestigationIncident Response
Security Testing
Nmap ReconHydra Brute-Force SimulationTelnet (Cleartext Risk)Detection ValidationCustom Detection Rules
Systems & Scripting
Windows SysinternalsSysmonProcess ExplorerAutorunsPowerShellActive DirectoryLinuxBashProxmox VE
Frameworks & Governance
NIST CSF 2.0MITRE ATT&CKSTRIDE Threat ModelingPhilippine NCSP 2023–2028Group Policy (GPO)RBAC
Training Platforms
LetsDefendVirusTotalAny.runMXToolbox
Documentation & Communication
Technical DocumentationConcept PapersSWOT AnalysisNarrative ReportsExecutive SummariesStakeholder CommunicationGoogle Workspace
06 — Awards & Leadership

Recognition & Leadership

Academic honors, community service and student leadership at De La Salle Lipa.

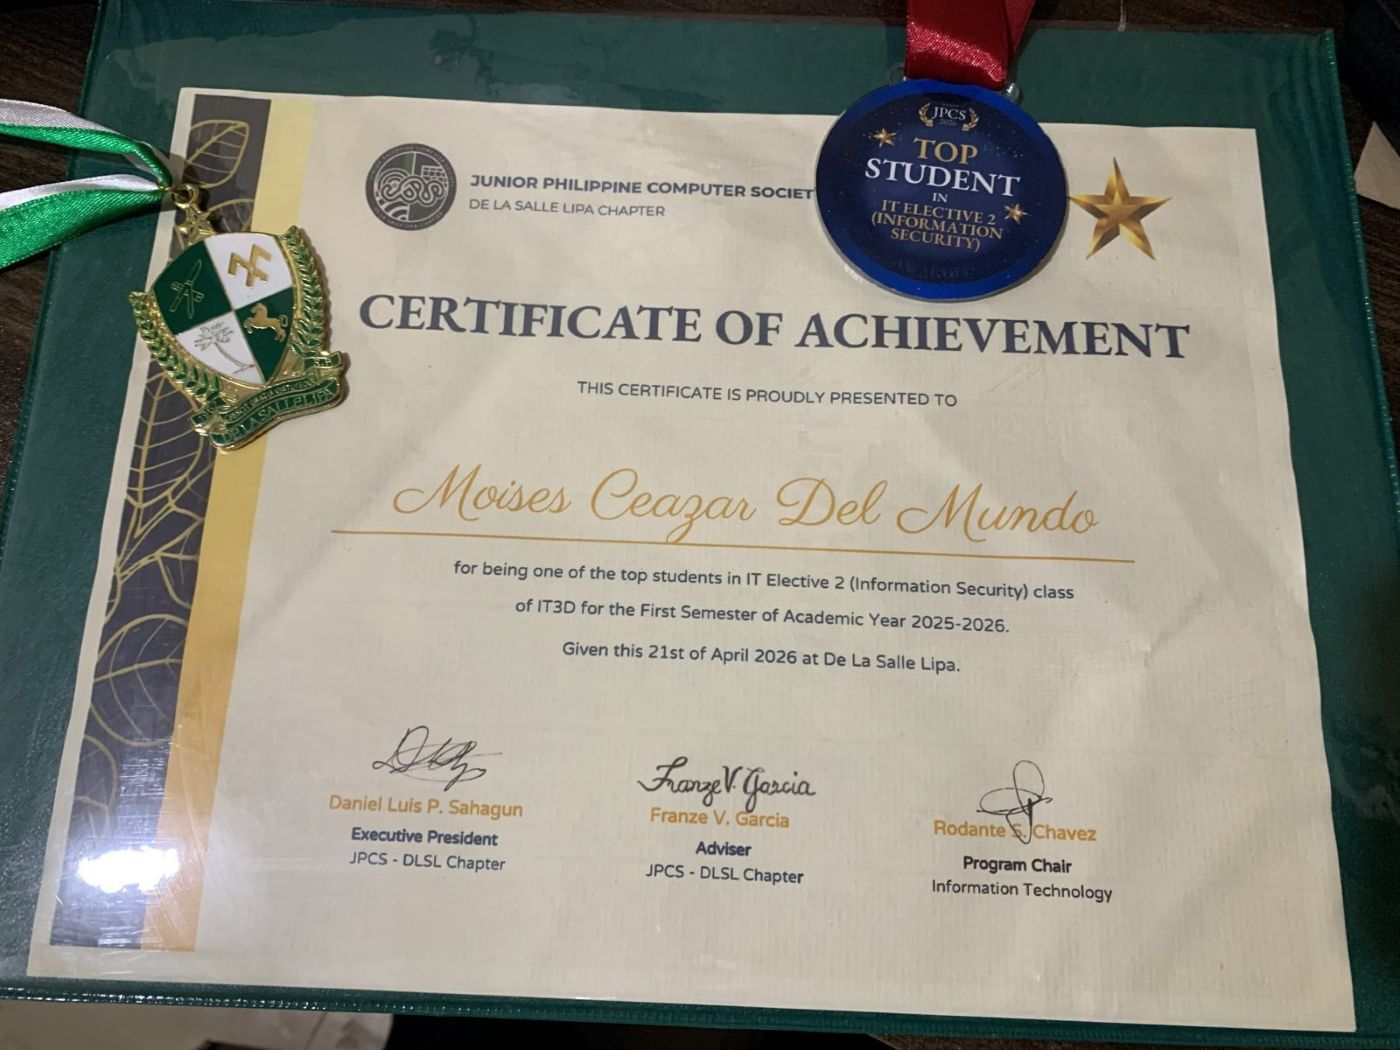
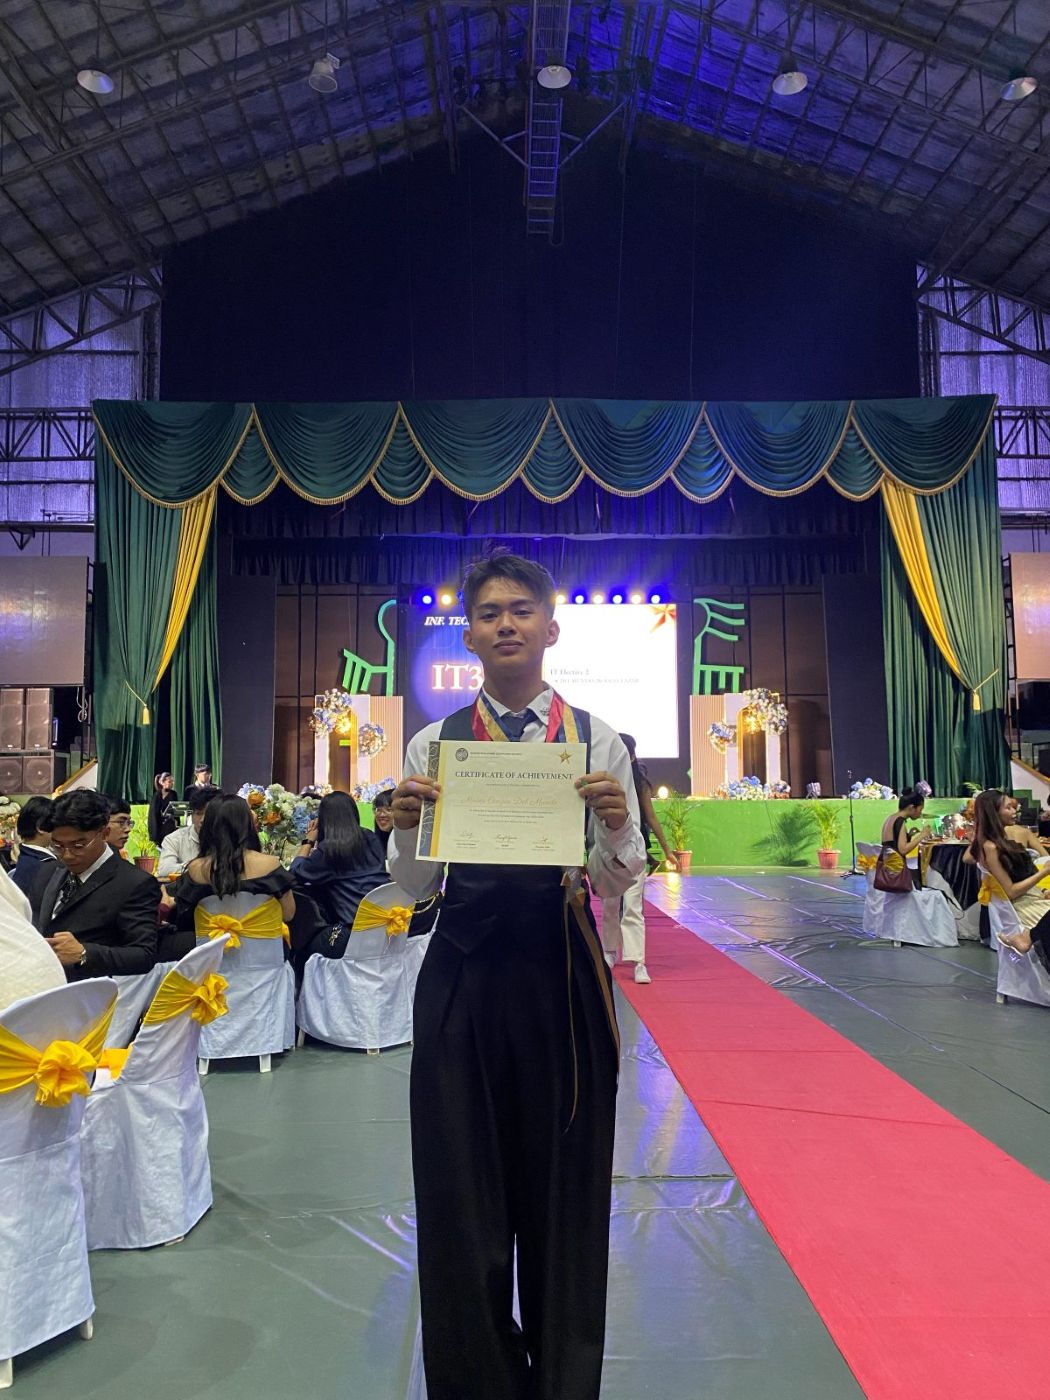
🏅 Top Student Awardee
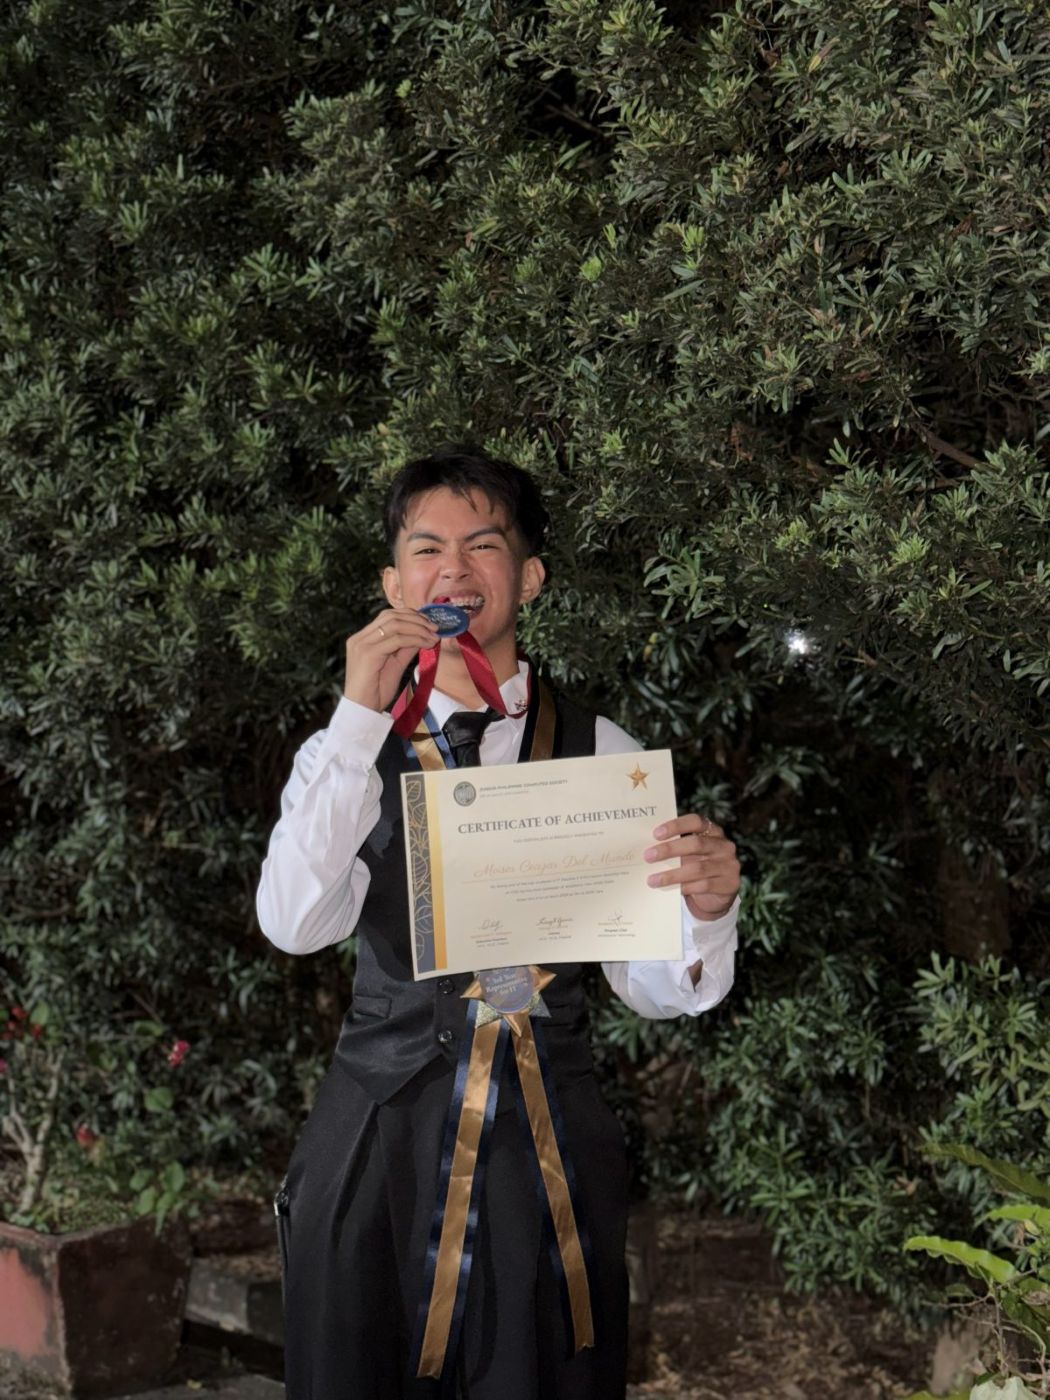
Academic Honors · JPCS – DLSL Chapter · April 21, 2026

Top Student — IT Elective 2 (Information Security): Security Planning, Implementation & Audit

Recognized as one of the top students in the IT Elective 2 (Information Security) class of IT3D for the First Semester of Academic Year 2025–2026, presented by the Junior Philippine Computer Society – De La Salle Lipa Chapter and the IT Program.
🎖️ NSTP Lingkod Awardee
Community Service · NSTP · De La Salle Lipa · June 14, 2024

NSTP Lingkod Award — Community Service Learning

Spearheaded our NSTP group's community service project at a local public school, teaching students basic computer skills: how to navigate and use a computer, and how to work with Microsoft Office apps like Word. Recognized for exceptional dedication and service to the community.
🤝 Student Leadership
Leadership · Junior Philippine Computer Society – DLSL Chapter

JPCS Officer — Internal Affairs & IT Student Representation

Project Head, Internal Affairs (IT)
Current · AY 2026–2027
3rd Year IT Representative
AY 2025–2026

Lead student committees organizing department-wide IT workshops, technical seminars and academic competitions for 200+ attendees. Write the paperwork behind each event for administrative approval — concept papers, SWOT analyses, narrative reports and executive summaries — and handle stakeholder communication and promotional media.
Event PlanningConcept PapersSWOT AnalysisNarrative ReportsExecutive SummariesGoogle Workspace
07 — Credentials

Certifications & Badges

Click any item to view the full certificate or badge.
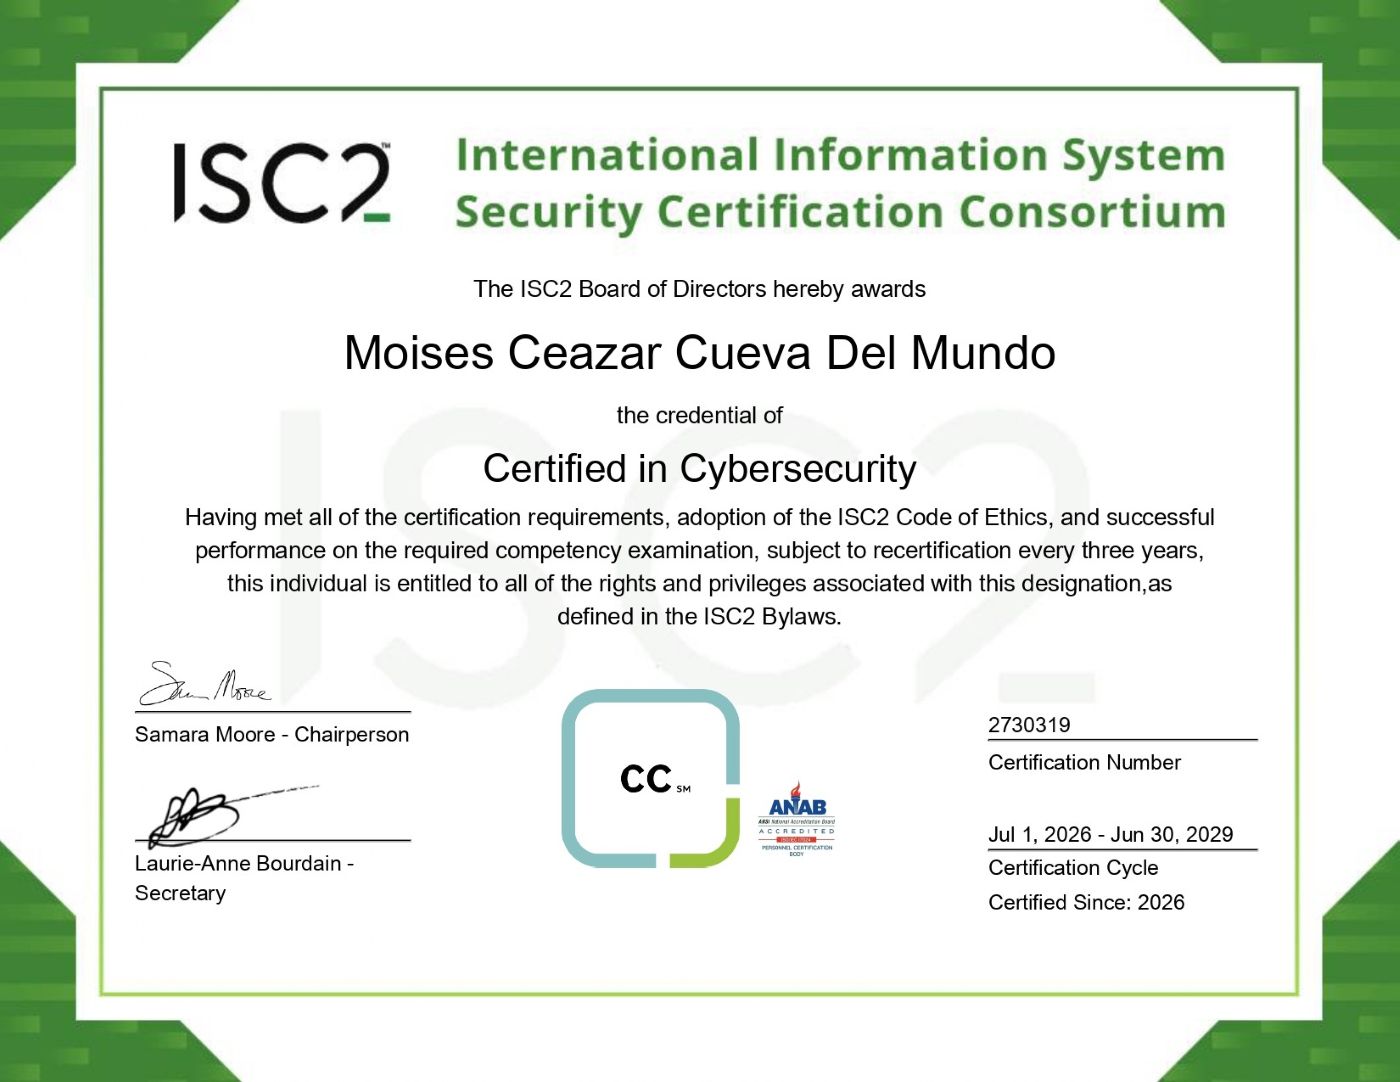
ISC2
ISC2
Certified in Cybersecurity (CC)
Jun 2026 · Valid to 2029Verify on Credly ↗
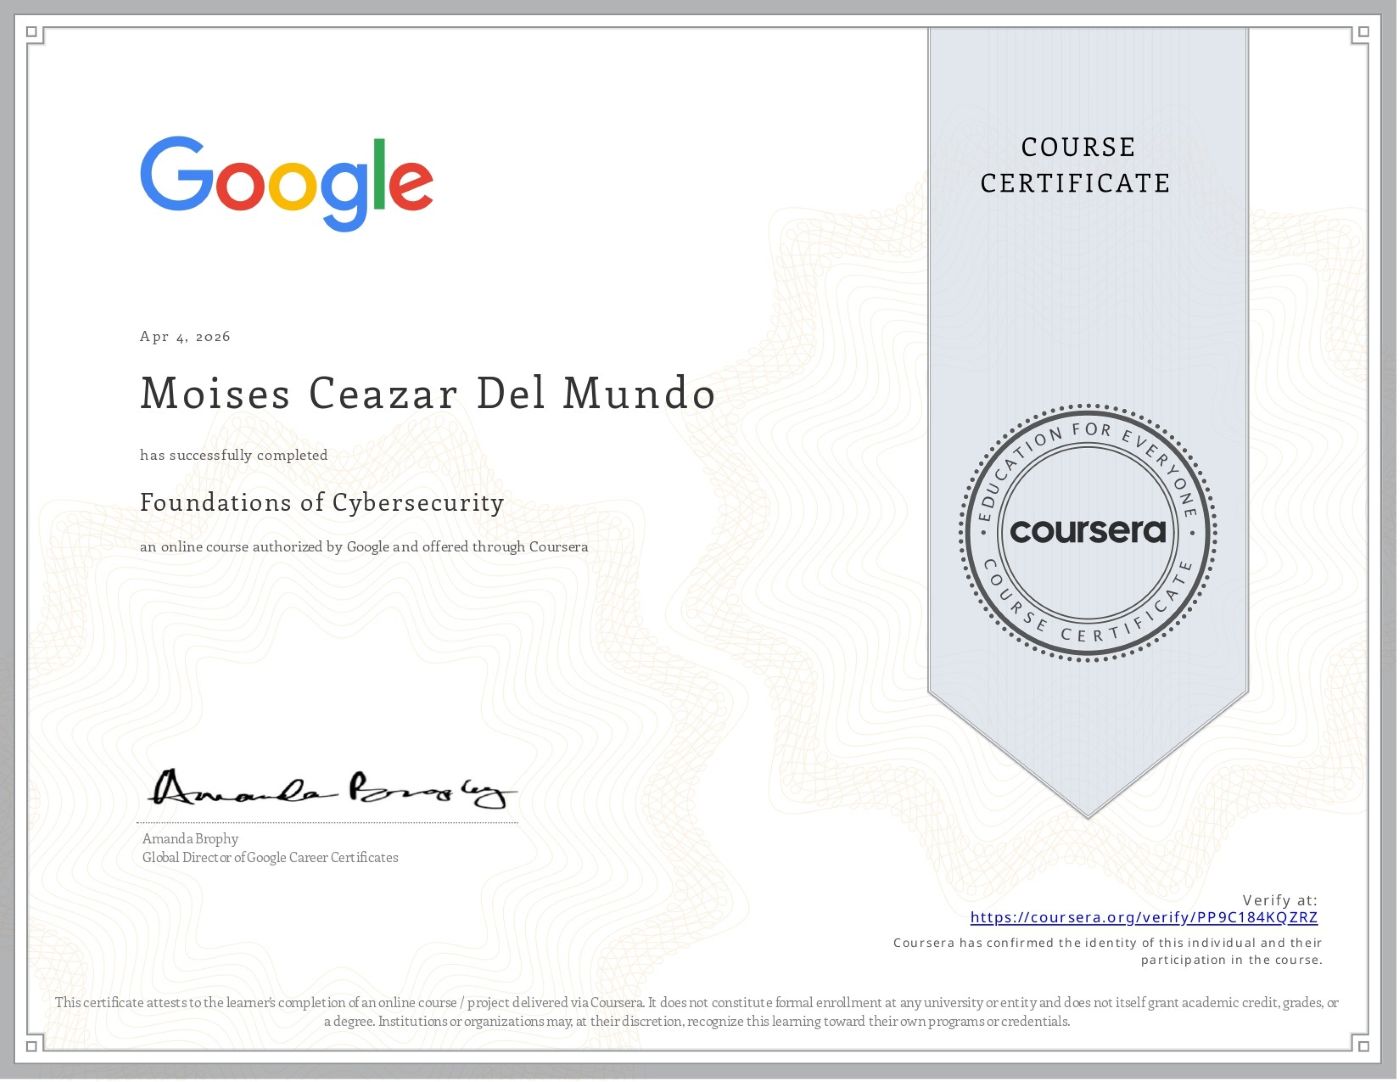
Foundations
Google / Coursera
Foundations of Cybersecurity
Apr 2026Verify ↗
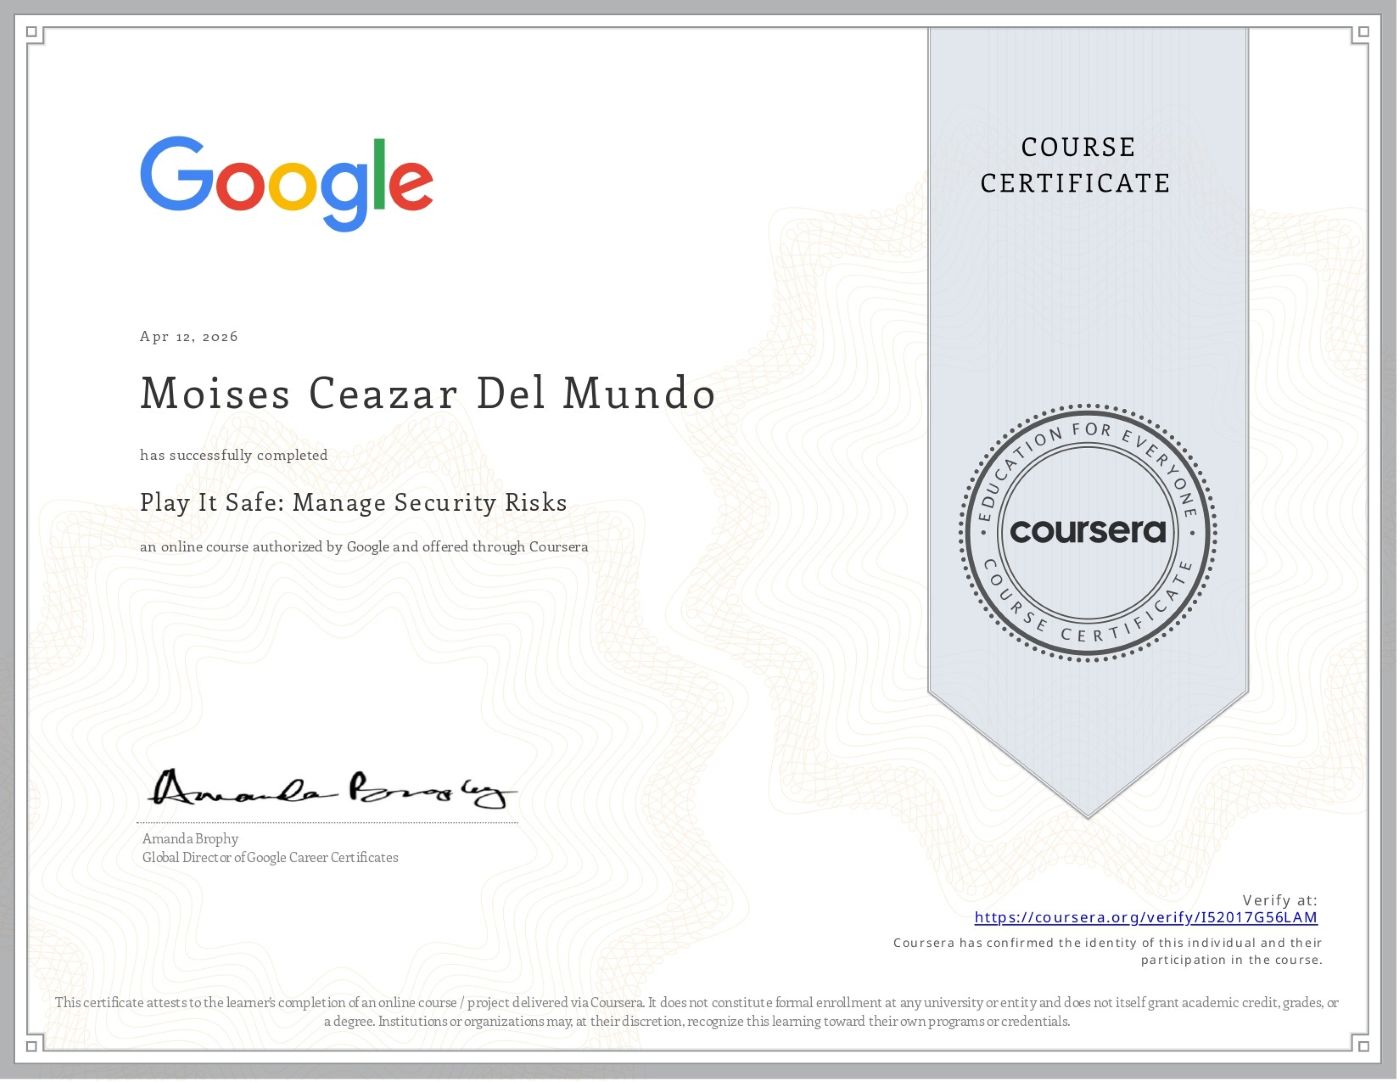
Play It Safe
Google / Coursera
Play It Safe: Manage Security Risks
Apr 2026Verify ↗
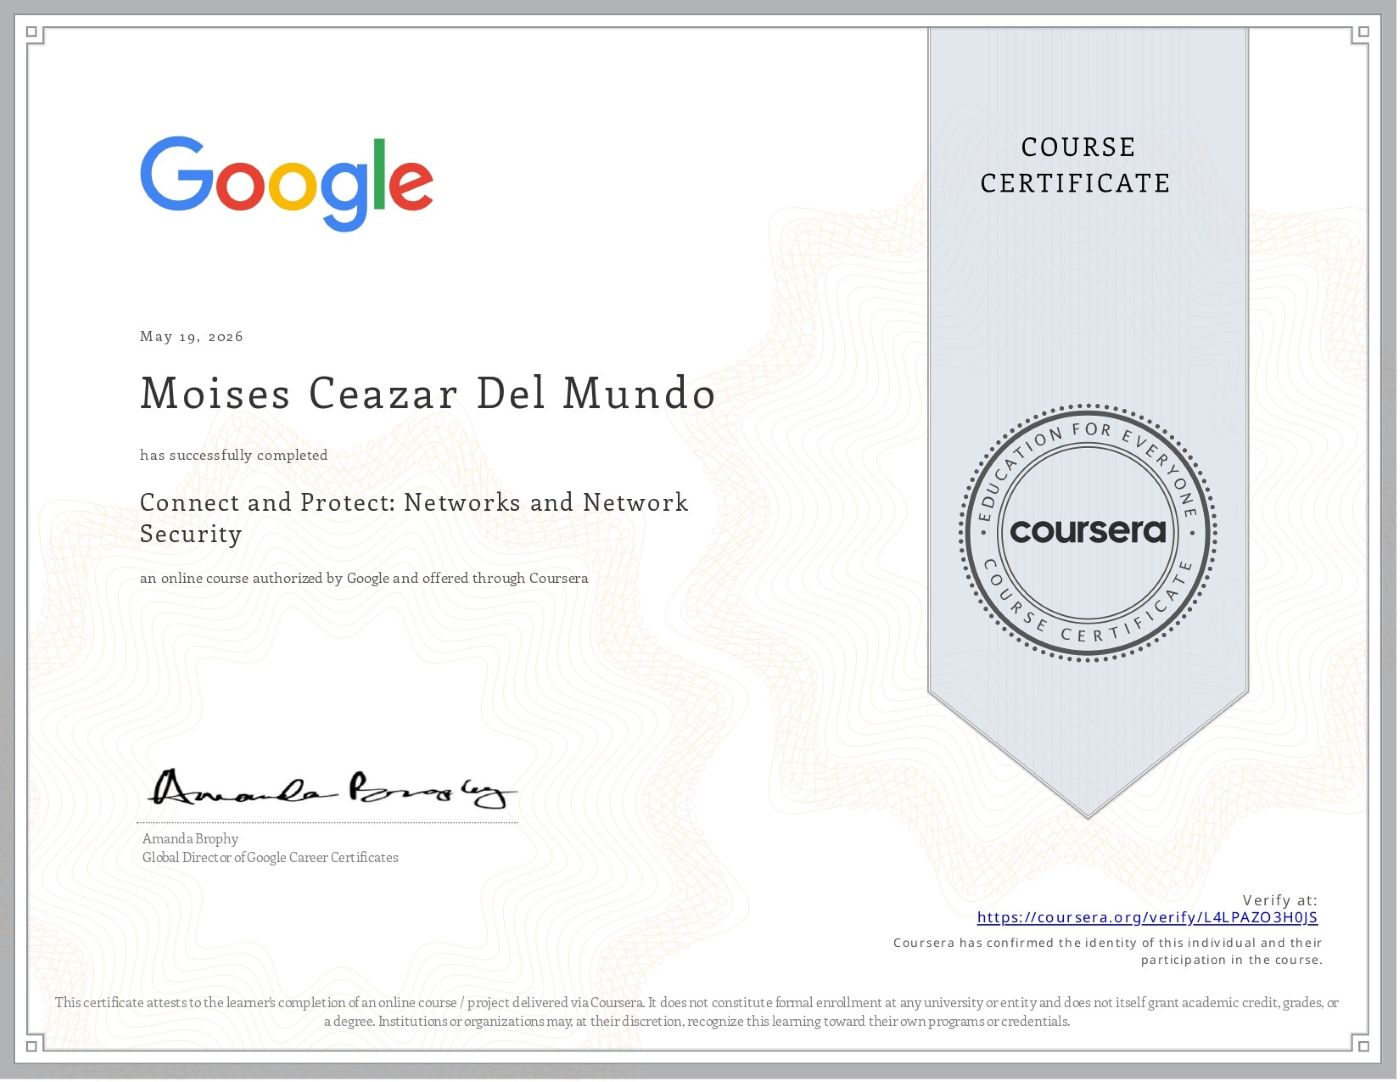
Networks
Google / Coursera
Connect & Protect: Networks & Security
May 2026Verify ↗
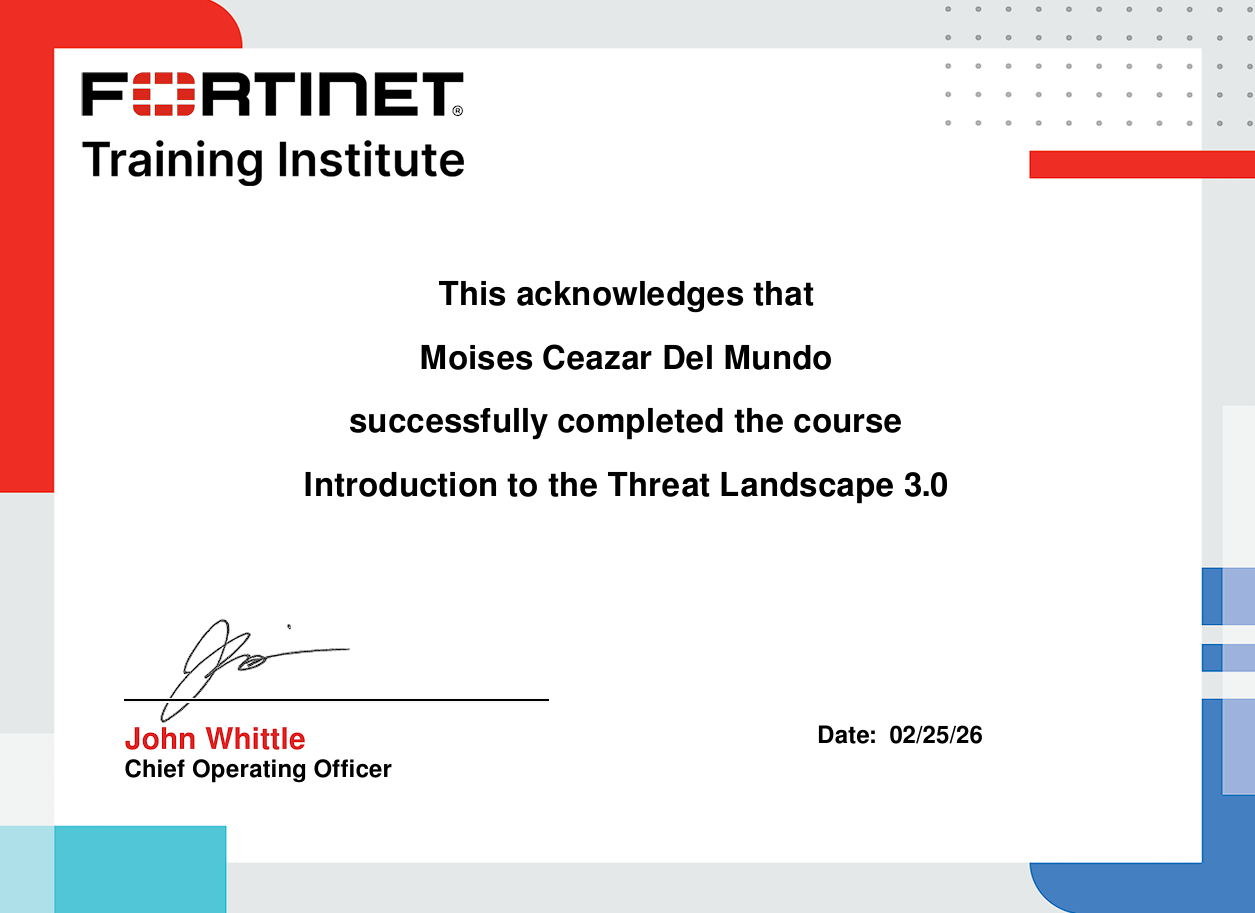
Fortinet
Fortinet
Introduction to the Threat Landscape 3.0
Feb 2026 View
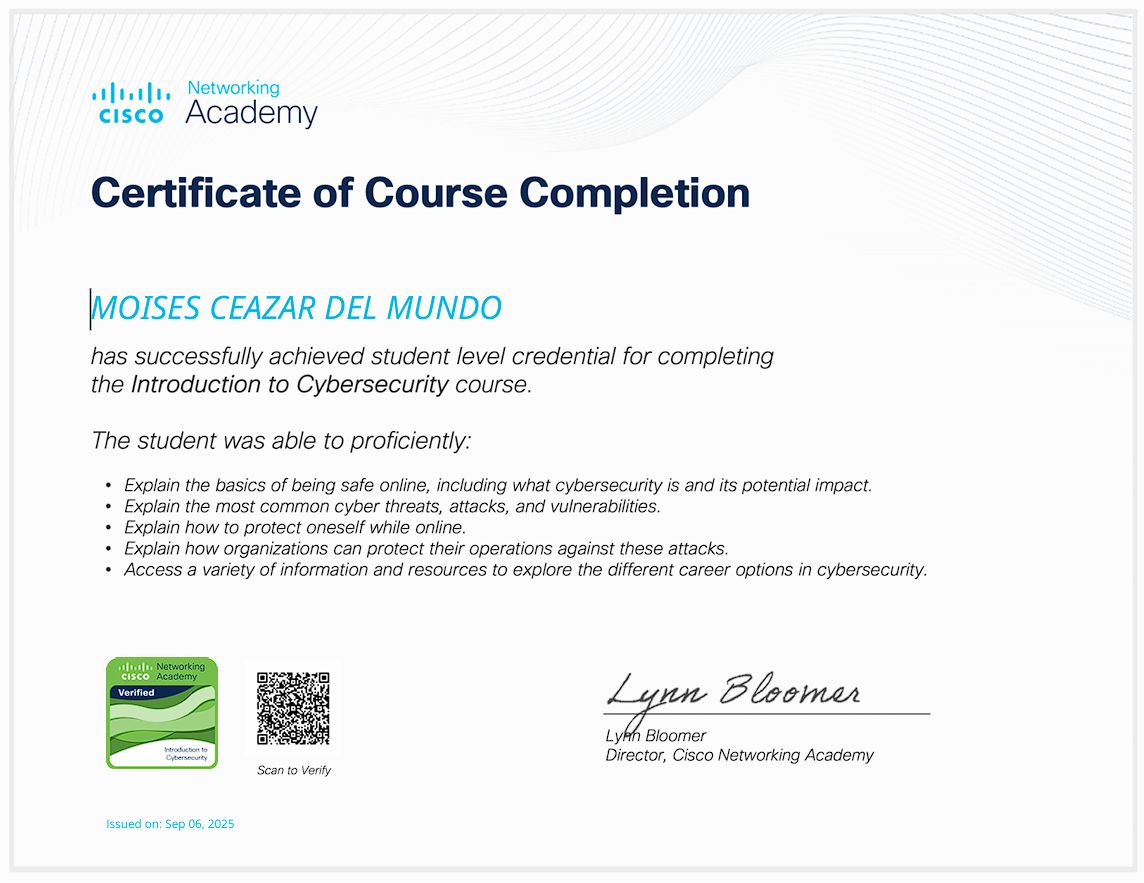
Cisco
Cisco Networking Academy
Introduction to Cybersecurity
Sep 2025 View
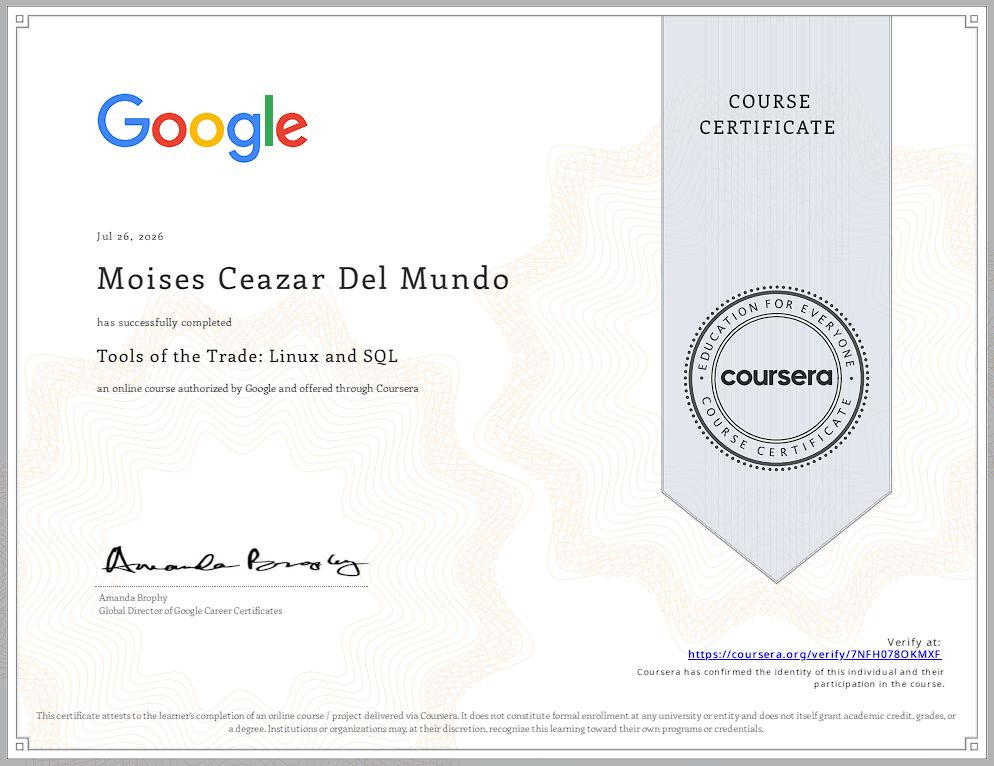
Linux and SQL
Google / Coursera
Tools of the Trade: Linux and SQL
Jul 2026 View
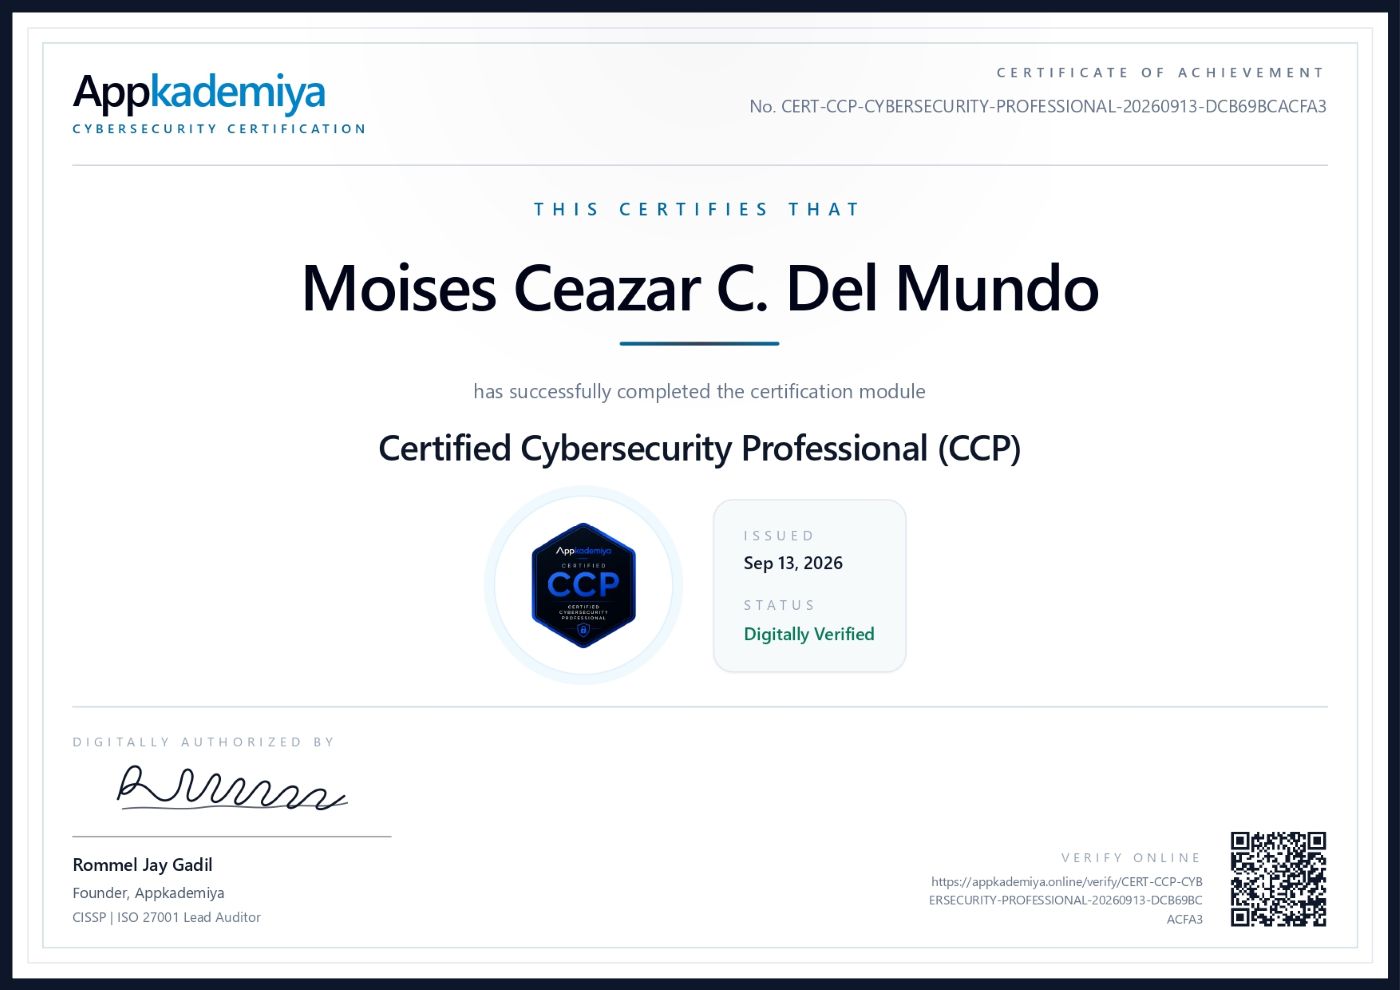
Certified Cybersecurity Professional (CCP)
Appkademiya
Certified Cybersecurity Professional (CCP)
Sep 2026Verify ↗
LetsDefend Public Profile
app.letsdefend.io/user/moihackthebox
6
Badges
SOC
Member
View Profile →
First Blood
First Blood
Investigated First Incident
Feb 19, 2026LetsDefend
SOC Member
SOC Member
SOC Fundamentals Course
Feb 20, 2026LetsDefend
Incident Handler
Incident Handler
Investigated 5 Different Incidents
Feb 21, 2026LetsDefend
Phishing Expert
Phishing Expert
Phishing Email Analysis Course
Mar 25, 2026LetsDefend
Malware Analyzer
Malware Analyzer
Malware Analysis Fundamentals
Mar 26, 2026LetsDefend
Incident Management
Incident Management
Incident Management 101 Course
Mar 27, 2026LetsDefend
08 — Writeups

SOC Investigations

Documented alert triage, threat analysis & incident investigations.

CRITICAL
SOC274 — Palo Alto PAN-OS Command Injection (CVE-2024-3400)
GlobalProtect login exploit · Command injection · MITRE T1190
WEB ATTACK→
CRITICAL
SOC336 — Windows OLE Zero-Click RCE (CVE-2025-21298)
Malicious RTF attachment · Zero-click RCE · C2 callback
MALWARE→
CRITICAL
SOC338 — Lumma Stealer: DLL Side-Loading via ClickFix Phishing
Fake Windows 11 upgrade lure · ClickFix · DLL side-loading
DATA LEAKAGE→
CRITICAL
SOC342 — CVE-2025-53770 SharePoint ToolShell Auth Bypass & RCE
Unauthenticated ToolPane.aspx POST · Auth bypass · RCE
WEB ATTACK→
HIGH
SOC287 — Arbitrary File Read on Check Point Security Gateway (CVE-2024-24919)
Path traversal · /etc/passwd read · Successful exploitation
WEB ATTACK→
MEDIUM
SOC153 — Suspicious PowerShell Script Executed
Malicious payload_1.ps1 · Active C2 communication · MITRE T1059.001
MALWARE→
MEDIUM
SOC251 — Quishing Detected (QR Code Phishing)
Fake MFA update lure · QR code decode · Typosquatted sender
EXCHANGE→
MEDIUM
SOC282 — Phishing Alert: Deceptive Mail Detected
Free coffee voucher lure · Malicious ZIP payload · User execution
EXCHANGE→
MEDIUM
SOC326 — Impersonating Domain MX Record Change Detected
Typosquatted domain · New MX record · Threat intel lookup
THREAT INTEL→
MEDIUM
SOC335 — CVE-2024-49138 Exploitation Detected
Masquerading svohost.exe · PowerShell parent · Privilege escalation
PRIVILEGE ESCALATION→
LOW
SOC257 — VPN Connection from Unauthorized Country
Auth logs · Geo-IP anomaly · Unauthorized VPN access
UNAUTHORIZED ACCESS→
09 — Contact

Let's Connect

Looking for a
driven intern?

I'm actively looking for a Cybersecurity or SOC Analyst OJT / internship in the Philippines. Hands-on lab experience, real certifications, and the discipline to learn fast.

Available Now

Internship Profile

Cybersecurity or SOC Analyst OJT. Open to on-site, hybrid, or remote in the Philippines.

SchoolDe La Salle Lipa
DegreeBSIT, Major in Information Security
GraduationExpected June 2027
GWA3.38
LetsDefendmoihackthebox · 6 Badges
ResponseWithin 24 hours